

Endpoint management is the practice of centrally inventorying, configuring, updating, and monitoring every device that connects to your network. Those devices include laptops, desktops, phones, tablets, and other connected equipment. The goal is simple: keep each device in a known, supported, and secure state.
If you manage more than a handful of devices, you already know how quickly things drift. One laptop misses an update. A phone still enforces a password policy from two years ago. A former contractor’s tablet can still reach company email.
This guide covers what endpoints are, how management platforms work, where MDM, EMM, UEM, and RMM differ, how endpoint management differs from endpoint security, and how to start a program that fits a small team. It draws on vendor documentation and public frameworks, cited where relevant. None of these tools were tested hands-on for this article, so treat the steps as a starting framework rather than a lab-tested recipe.
What is Endpoint Management?
Endpoint management is a set of practices and tools that IT and security teams use to control devices from one console. Instead of configuring each laptop by hand and checking each phone one at a time, administrators see every device in one place, push settings and software, and track whether devices meet the organization’s rules.
The word “endpoint” describes where these devices sit: at the edge, where people connect to company systems. That position makes every device a possible entry point for an attacker and a possible exit point for data. Managing the endpoint means managing that boundary before someone else exploits it.
Scope matters here. Endpoint management covers which devices exist, how they are configured, what software they run, whether they are current, and what happens when a device is lost, replaced, or retired. It is less a product than a repeatable process that good tools support.
What counts as an endpoint?
An endpoint is any device that connects to a network and can be used to reach company systems or data. The term is broader than many people assume.
- Laptops and desktops used by employees, contractors, and developers.
- Smartphones and tablets, whether company-owned or personal (BYOD).
- Servers and virtual machines, when your team defines scope that way.
- Printers, scanners, and kiosks joined to the network.
- IoT devices such as smart displays, sensors, and conference room equipment.
Sophos’s overview of endpoint management makes the same point: laptops, desktops, smartphones, tablets, and IoT devices are common entry points for cyberattacks. That is why the definition of “endpoint” is worth arguing about early. A device nobody manages is a device nobody protects.
How does Endpoint Management work?
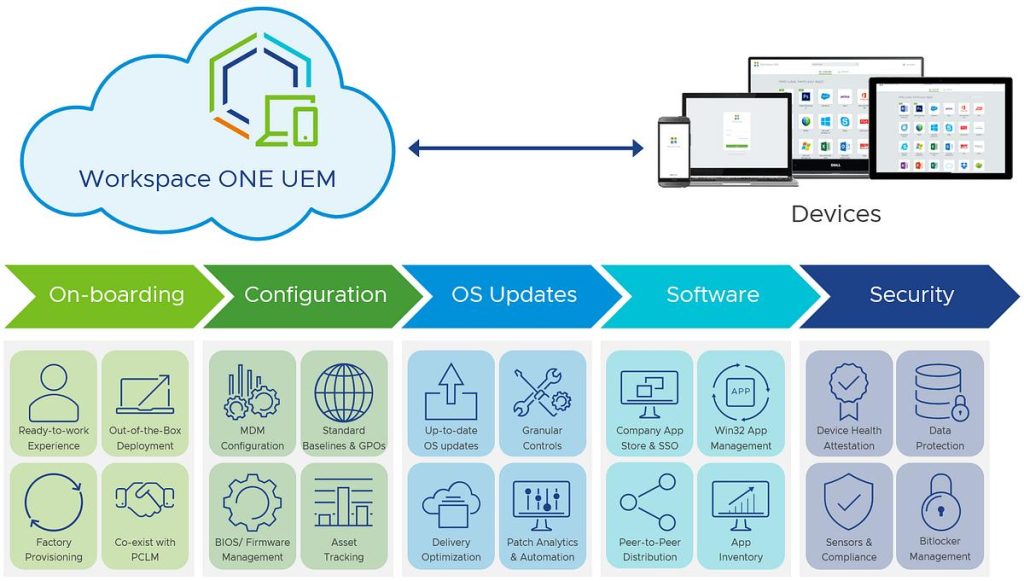
Most platforms work through a lightweight agent installed on each device. The agent checks in with a central console, which lets administrators see status and send instructions. Some platforms manage devices without an agent by using built-in operating system features, which is common for mobile devices.
The device lifecycle
A managed device typically moves through six stages:
- Enrollment. The device registers with the platform — at first setup, when a new device is issued, or when a personal device is approved for work use.
- Baseline configuration. It receives standard settings: password rules, encryption, network profiles, certificates, required applications.
- Policy enforcement. The platform applies security and compliance rules, and reapplies them when a device drifts.
- Maintenance. Updates and patches deploy, software is installed or removed, health gets monitored.
- Support. Administrators troubleshoot, sometimes taking remote control with the user’s permission.
- Retirement. Access is removed, data is wiped, the record is closed.
That lifecycle is why endpoint management outgrows any single tool. Every stage touches security, compliance, and cost at once.
Core functions
| Function | What it does | Why it matters |
|---|---|---|
| Inventory | Tracks devices, hardware, operating systems, software, owners | You can’t protect what you can’t see |
| Configuration | Applies consistent settings across devices | Reduces weak or inconsistent setups |
| Software deployment | Installs and updates approved applications | Keeps tools current, limits shadow IT |
| Patch management | Delivers operating system and application updates | Closes known flaws before attackers use them |
| Security enforcement | Requires encryption, passcodes, firewalls | Protects data on devices that leave the office |
| Remote support | Lets IT troubleshoot from anywhere | Supports remote and hybrid work |
| Compliance reporting | Shows which devices meet standards | Provides audit and customer evidence |
| Lost device response | Locks, locates, or wipes a device | Limits damage when hardware disappears |
Sophos groups the same ground under inventory management, configuration management, software deployment, software patch management, and security monitoring and reporting. Those functions are the floor everything else stands on.
What a management platform includes
Vendors name things differently, but the building blocks are consistent.
| Component | Role |
|---|---|
| Management console | Central dashboard for viewing devices, applying policies, running reports |
| Agent or native OS channel | The link between device and console — installed software on some platforms, built-in OS features on others |
| Device inventory | Database of devices, hardware, operating systems, software, owners |
| Policy engine | Stores rules, applies them to device groups, reapplies them on drift |
| Software distribution | Delivers approved applications, packages, and scripts |
| Patch service | Tracks available updates and deploys them on a schedule |
| Reporting engine | Surfaces compliance status, overdue updates, unmanaged devices |
| Integrations | Connects to identity providers, ticketing, and security tools |
Integrations often decide whether a program works outside the console. If your management platform can’t share device compliance with your identity provider, you can’t block an unmanaged laptop from reaching company email. That gap becomes obvious the moment you try to enforce anything in the zero-trust section below.
Features worth checking
The available list depends on the vendor and the operating system, so confirm current product documentation before planning around any single capability.
- Enrollment and provisioning. New devices arrive with the right settings from first boot, often without manual imaging.
- Remote lock, wipe, and locate. Some platforms can wipe only company data on a personal device.
- Application catalog and self-service portal. Users install approved software themselves, which cuts support tickets.
- Certificate and network profile deployment. Wi-Fi, VPN, and certificate settings arrive preconfigured.
- Compliance dashboards. Encryption, password, and update status at a glance.
- Remote control. IT views or controls a device with the user’s consent.
- Scripting and automation. Repeatable tasks — clearing a cache, checking disk health — run across a device group.
- Alerts. Notifications when a device goes offline, drops out of compliance, or reports a fault.
- Container or app-level management. Protects corporate apps and data on personal devices without managing the whole device.
Feature parity across Windows, macOS, iOS, Android, and Linux is uneven. Test each feature on every platform you support before promising it to users — the gap is usually discovered by the person whose phone doesn’t support it.
Location tracking and monitoring need written rules before they need a toggle. Tell people what the company can see and when. Some jurisdictions regulate employee monitoring, so involve legal or HR before switching those features on.
MDM vs EMM vs UEM vs RMM: which one do you need?
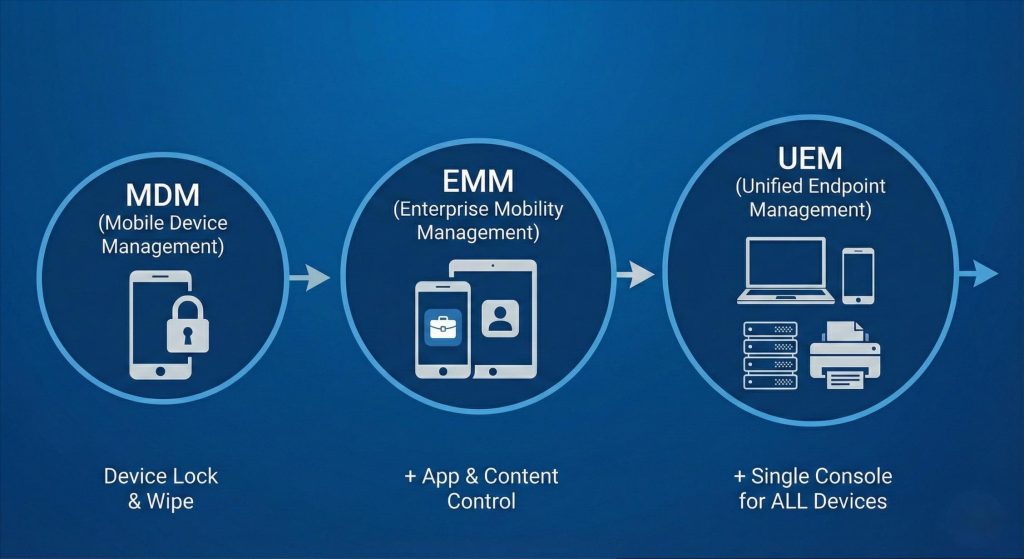
These labels get used loosely. Here’s what each one usually means.
| Category | Full name | Typical focus | Best fit |
|---|---|---|---|
| MDM | Mobile Device Management | Phones and tablets: enrollment, passcodes, remote wipe, app deployment | Mobile-first environments |
| EMM | Enterprise Mobility Management | Mobile devices plus app-level controls and data containers | BYOD programs that protect corporate data without controlling the whole phone |
| UEM | Unified Endpoint Management | Laptops, desktops, mobile, and other endpoints in one console | Mixed fleets that want a single pane of glass |
| RMM | Remote Monitoring and Management | Monitoring, remote support, maintenance — common among managed service providers | Teams administering many client systems |
The categories overlap, and vendors routinely market one product under several of these names. Sophos lists MDM, EMM, UEM, and client management tools as the common ways organizations implement endpoint management. Labels matter less than your device mix.
A short selection guide:
- Mostly phones and tablets? Start with MDM or EMM.
- Laptops, desktops, and mobile in one fleet? Look at UEM.
- Managing many customer environments, or a small IT team with a heavy remote support load? Look at RMM.
- Contractors and staff on personal laptops? Prioritize app-level or container-based controls that protect company data without taking over the whole machine.
What is Endpoint Security, and how is it different?
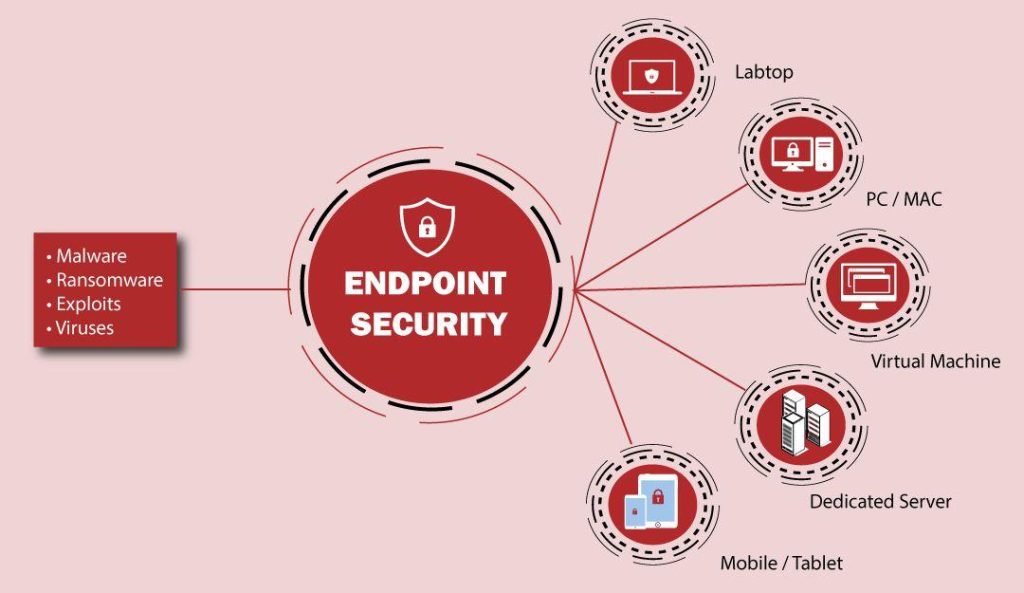
Endpoint security is the practice of protecting devices from threats: malware, ransomware, phishing payloads, and misuse of stolen credentials. It focuses on detecting and stopping attacks rather than on configuring devices.
The tooling has layered up over time:
- Antivirus matches files against known malicious signatures. It is useful against common malware and weaker against fileless attacks and abuse of legitimate tools.
- Endpoint protection platforms (EPP) bundle prevention: antivirus, firewall, device control, application control.
- Endpoint detection and response (EDR) watches endpoint activity continuously, flags suspicious behavior, and supports investigation and response such as isolating a device.
Kaspersky’s EDR explainer draws the line usefully. It notes that the term was coined by Gartner in 2013, and that antivirus “can only act on threats and anomalies that they know already exist,” while EDR tools “identify new exploits as they are running and detect suspicious activity by an attacker during an active incident.”
No single tool covers everything. Security tools need accurate device data to make good decisions; management tools need security signals to know which devices need attention first. Our comparison of endpoint security and antivirus covers the tool-level differences in more detail.
Side by side
People mix these two disciplines up constantly. They work together, but they do different jobs.
| Endpoint management | Endpoint security | |
|---|---|---|
| Primary goal | Operational control and device health | Threat prevention, detection, and response |
| Focus | Configuration, updates, software deployment | Malware defense, threat detection, data protection |
| Typical tools | RMM, MDM, UEM | EDR, MDR, XDR, firewalls, SIEM |
| Outcome | Stable, compliant, up-to-date devices | Devices defended against attack |
ConnectWise’s comparison of the two is blunt about the risk: “relying on one without the other creates visibility and protection gaps.” Without endpoint security, even well-managed devices can be compromised. Without endpoint management, outdated or misconfigured systems stay vulnerable.
In practice, the handoff runs both ways. A management tool spots a remote laptop missing its latest patch. A workflow pushes the update while a security tool watches for exploit attempts against that specific flaw. If something looks wrong, the security tool isolates the device and management supplies the remote access to fix it. Good programs wire those steps together instead of leaving them as a ticket someone reads on Friday.
Why does Endpoint Management matter?
It isn’t an IT convenience. It shapes security, compliance, cost, and how easily people can do their jobs.
Unpatched software stays a favorite target. Attackers go where the fixes haven’t landed. The CISA Known Exploited Vulnerabilities catalog, which CISA describes as “the authoritative source of vulnerabilities that have been exploited in the wild,” exists precisely because knowing which flaws are being used changes the order in which you patch.
Inventory gaps are blind spots. CIS Control 1, Inventory and Control of Enterprise Assets, asks organizations to “actively manage (inventory, track, and correct) all enterprise assets,” including end-user devices, network gear, IoT devices, and servers, whether they sit on-premises, remotely, or in cloud environments. If you don’t know a device exists, you can’t patch, configure, or protect it.
Hybrid work stretched the perimeter. Devices connect from homes, cafés, and airports. IT can’t walk over to fix a problem or enforce a setting physically. Remote visibility and control stopped being optional.
Lost and stolen devices are routine. Remote lock and wipe limit the damage while the laptop is still in a taxi. Without them, data stays reachable until someone thinks to ask.
Compliance runs on evidence. Regulations and customer contracts increasingly expect proof of control over how data is accessed and protected. Management reports generate that evidence without a week of spreadsheet archaeology.
BYOD needs boundaries. Personal phones and laptops reach company mail and files. You need controls that protect corporate data without turning an employee’s phone into company property.
What should an endpoint management policy cover?
A policy is a written rule about how devices are configured, used, and protected. Tools enforce policy; people have to write it first. Without written rules, your settings are whatever the last administrator happened to prefer.
A workable policy set covers:
- Acceptable use. What devices may be used for, which software is allowed, what isn’t. Our guide to building an acceptable use policy walks through the structure.
- Device security baseline. Required settings: disk encryption, screen locks, firewalls, minimum operating system versions.
- BYOD terms. Which personal devices may reach company systems, what the company can and can’t see, and what happens at offboarding.
- Software approval. How applications get requested, reviewed, and approved, and which categories are blocked outright.
- Patch timelines. Deadlines for security updates, tiered by severity and exploit status.
- Data protection. Rules for storing, sharing, and removing company data. Our data loss prevention best practices cover adjacent controls.
- Lost and stolen devices. Who reports, how fast, and what happens to the device and its data.
- Offboarding and retirement. How access is revoked and how devices are wiped, reassigned, or recycled.
- Exceptions. How to request one, who approves, and when it expires.
Every policy needs an owner, a review date, and a named enforcement mechanism. Our vulnerability management policy example shows a structure that holds up in an audit.
A sample rule, hypothetical: “All company-issued laptops must use full-disk encryption and install security updates within 14 days of release. Devices that miss the window lose access to company email until they comply.”
Keep policies short. Long documents go unread, and a short policy people follow beats a thorough one nobody remembers exists.
How does remote device management work in practice?
Remote device management means administering devices you can’t reach physically. Nearly every organization needs it now: staff work from home and client sites, and contractors often supply their own equipment.
It handles the everyday work:
- Enrollment without a site visit. A new hire unboxes a device, enrolls remotely, and gets working settings without a desk setup appointment.
- Health checks. Online status, operating system version, free storage, compliance state.
- Patch delivery. Updates land whether the device sits in an office or on a home network, as long as it checks in.
- Troubleshooting. Screen view, diagnostics, service restarts — with the user’s permission.
- Lost device response. Lock or wipe before data travels further.
It also has friction points worth planning for:
- Offline devices. A laptop closed for a week receives nothing until it reconnects. Set check-in expectations and decide what happens when a device stays dark too long.
- Bandwidth. Large updates strain home connections. Use scheduling and delivery optimization where supported.
- Consent and privacy. Remote sessions should be visible to the user, logged, and scoped to the task.
- Unmanaged devices. Contractors and personal devices may never enroll. Decide their access in advance instead of improvising under pressure.
One practice that pays off: set a maximum time a device can sit out of compliance before its access is restricted. That converts remote management from a reporting exercise into an actual control.
How should patch management work on endpoints?
Patch management is the process of finding, testing, and installing updates for operating systems, applications, and firmware. On endpoints it matters disproportionately, because devices run a long tail of software and nearly all of it needs updates.
A process that holds up:
- Inventory. Know which operating systems, browsers, plug-ins, and applications each device runs. Third-party applications are usually the widest gap.
- Assess. Check vendor advisories and severity ratings, and flag flaws under active exploitation. The CISA catalog is the practical filter for what deserves attention this week.
- Prioritize. Rank by risk, exposure, and asset importance. Our guide to prioritizing vulnerability remediation describes a tiered approach.
- Test. Deploy to a small pilot group. Watch for application conflicts, failed installs, and performance regressions.
- Deploy. Roll out in rings: pilot, wider group, full fleet. Schedule restarts so people can save their work.
- Verify. Confirm devices actually received the update. For critical systems, check installed versions directly rather than trusting the deployment report.
- Report. Track compliance, overdue devices, and approved exceptions.
Two areas deserve their own attention. Browsers and document readers are frequent targets, so treat their updates with the same urgency as operating system patches. Mobile devices need minimum operating system requirements, and older phones may need retiring once a vendor stops shipping updates.
For automation, our guide to an automated patch management process covers scheduling and verification. Teams that also scan for weaknesses can use vulnerability scanning to confirm which endpoints still need work.
How does Endpoint Management support zero trust?
Zero trust rests on one idea: don’t trust a request by default, even from inside the network.
NIST Special Publication 800-207, Zero Trust Architecture, published in August 2020, describes zero trust as “an evolving set of cybersecurity paradigms that move defenses from static, network-based perimeters to focus on users, assets, and resources.” Two details in its abstract matter for device work. Zero trust “assumes there is no implicit trust granted to assets or user accounts based solely on their physical or network location” or on who owns the device. And “authentication and authorization (both subject and device) are discrete functions performed before a session to an enterprise resource is established.”
Read those two lines together and the requirement is clear. The device has to prove itself, not just the person holding it. Endpoint management is what makes that proof possible, because someone has to know whether the device is managed, encrypted, current, and running the security software it claims to run.
Management tools supply those answers; the access layer consumes them as conditions. A compliant laptop reaches email and files. A noncompliant one gets limited access until it’s fixed. A device that hasn’t checked in for weeks loses access until someone confirms it’s still real.
Zero trust also depends on identity and least privilege. A managed device with weak account controls is still a liability. Our guide to zero trust security covers the wider model, and our piece on evaluating privileged access management solutions addresses the accounts that carry the most risk.
A realistic starting point for a small team:
- Require managed devices for email and core business systems.
- Turn on multi-factor authentication for every account.
- Block devices that fail critical checks, such as encryption or required security updates.
- Review access rules quarterly, and revoke access when people or devices leave.
Zero trust isn’t a purchase. It’s an accumulation of access rules that each close a specific gap.
What does a solid program include?
- A complete inventory. Every device, its owner, its operating system, its software, and its location where appropriate.
- Standard configurations. Defined baselines per device type, with documented exceptions and approvers.
- Patch and update policy. Timelines, severity tiers, and fleet-wide compliance tracking.
- Encryption and access controls. Disk encryption on laptops, screen locks on phones, strong authentication for company systems.
- Application control. What’s allowed, what’s required, what’s blocked.
- Remote support procedures. How IT takes control, what consent looks like, how users get notified.
- Offboarding. Revoke access, invalidate tokens, wipe or retrieve hardware.
- Reporting. Compliance, overdue updates, unmanaged devices, lost-device responses.
Our small business network security checklist covers adjacent basics if you’re starting from very little.
A worked example (hypothetical)
Consider a 40-person consulting firm. Staff use company laptops, personal phones for email, and a handful of contractor machines the firm doesn’t own. Devices live in a spreadsheet nobody updates. Some laptops haven’t been patched in months. Two former contractors still have access to shared files.
Step one is inventory: enroll everything that touches company systems, including personal phones, which get app-level management rather than full device control. Then a short baseline — disk encryption on laptops, passcodes on phones, security updates within two weeks. Contractor machines get a lighter policy that protects company files without managing the whole device.
Within a few months, the firm can answer basic questions quickly: which devices are behind, who installed unapproved software, whether a lost phone was wiped. Offboarding becomes a checklist instead of a memory test.
This example is illustrative, not a real company. Results depend on your environment, tooling, and staffing.
How do you start an endpoint management program?
You don’t fix everything at once. Staging beats a big-bang rollout.
Step 1: Assess what you have. List every device that connects to company systems — who uses it, what operating system it runs, whether it’s company-owned. Pay attention to the devices you can’t see yet; those are the point of the exercise.
Step 2: Set a baseline. Define minimum standards per device type. Start with four items — encryption, screen lock, updates, approved software — and expand later.
Step 3: Pick a tool category. Match your device mix to MDM, EMM, UEM, or RMM. Test with a small group before committing to a contract.
Step 4: Pilot. Enroll a few devices, ideally a mix of laptops and phones. Watch for user friction, failed deployments, and holes in your reports.
Step 5: Roll out in phases. Expand in stages and explain what changes: what the company can and can’t see on personal devices, who to call when something breaks.
Step 6: Enforce and report. Turn on enforcement for the critical policies first. Review compliance weekly, then monthly once the numbers settle.
Step 7: Review quarterly. Revisit the baseline, the device list, and the offboarding steps. Devices, software, and threats all move.
Quick answers
Is MDM the same as endpoint management?
No. MDM is one category within it, focused on phones and tablets. Endpoint management also covers laptops, desktops, and other connected devices, and usually spans the full device lifecycle.
We already run EDR. Do we still need endpoint management?
Yes, if you want devices configured and patched rather than only defended. Without management, outdated and misconfigured systems stay vulnerable no matter how good the detection is.
Can we manage personal phones without taking them over?
Usually, yes. EMM-class tools typically add app-level controls and data containers, so work data can be protected while the rest of the phone stays private. Confirm the specifics for each platform you support.
What’s the very first task?
The inventory. CIS Control 1 puts asset inventory first for a reason: you can’t patch, configure, or defend hardware you don’t know exists.
How long does a first rollout take?
It depends on fleet size, device mix, and how much of the baseline is already in place. Pilot a small group first, then expand in rings rather than setting a date for the whole fleet.
Conclusion
Endpoint management is the discipline that keeps devices visible, correctly configured, current, and recoverable. It starts with an accurate inventory and grows into standard settings, timely patching, enforcement, remote support, and clean offboarding. The right tool category depends on your fleet, but the goal doesn’t move: every device that touches company data should be known and managed.
Start with the inventory. Set a short baseline. Pilot it with a small group. Then measure what matters and keep reviewing as the environment shifts.
If you’re connecting this work to patching, our guide to an automated patch management process covers keeping updates moving. For the wider picture, the network security audit checklist helps you test whether your endpoint program fits the rest of your security work.
You May Also Like
 Data Security & Privacy
Tokenization vs Encryption: Key Differences and Best Practices
 Data Security & Privacy
How Encryption Works: A Practical Guide to Data Encryption Best Practices
 Cybersecurity
Why Strong Passwords Are Important?
 Data Security & Privacy
Endpoint Security vs Antivirus: Key Differences for Better Protection
 Network Security
What is Penetration Testing and Why Is It Crucial for Your Cybersecurity Strategy?
 Network Security
11 Best Free Penetration Testing Tools: Your Complete Guide for 2027
 Data Security & Privacy
The Importance of Vulnerability Management and Attack Surface Management
 Cybersecurity
Effective Strategies for Prioritizing Cybersecurity Vulnerability Remediation
 Web Development
