


Penetration testing, often called pen testing, is an authorized security assessment in which a tester simulates real-world attack techniques to find and validate weaknesses in an organization’s systems. The goal isn’t to break things or collect a long list of scanner alerts. It’s to find out whether a weakness can actually be used, what an attacker could reach, and what the organization should fix first.
A test may cover a public-facing website, an internal network, a cloud environment, a mobile app, an API, or a wireless network. The exact scope depends on the organization’s risks and the agreement with the tester. A well-planned engagement also sets clear limits so testing doesn’t expose real customer data or interrupt important services.
For example, a web application may appear secure because it uses HTTPS and requires users to sign in. A penetration tester might still discover that changing an account ID in a request lets one customer view another customer’s records. That’s a broken access control issue. The important finding isn’t simply that a parameter can be changed; it’s that the weakness exposes information belonging to other users.
This guide explains what penetration testing can and can’t tell you, how an engagement works, which types and tools are commonly used, what a useful report should contain, and how to choose a provider. It also explains how penetration testing relates to vulnerability scanning and common compliance requirements.

What Is Penetration Testing?
Penetration testing is a controlled, authorized attempt to exploit security weaknesses in a defined target. A qualified tester combines manual investigation with tools to see whether vulnerabilities can be chained together and what access they could provide.
That last point matters. A scanner might report an outdated service, a weak configuration, or a potentially vulnerable software version. A penetration test investigates whether the issue is reachable and exploitable in the agreed test environment. The tester then documents the evidence and the likely impact without going beyond the approved rules of engagement.
Penetration testing is not the same as an ordinary security scan, a compliance checklist, or a guarantee that a system is secure. It is a time-bound assessment of specific assets under specific conditions. A clean report means the testers did not identify a reportable weakness within that scope and testing window. It does not prove that no vulnerability exists.
What Is the Difference Between Penetration Testing and Vulnerability Scanning?
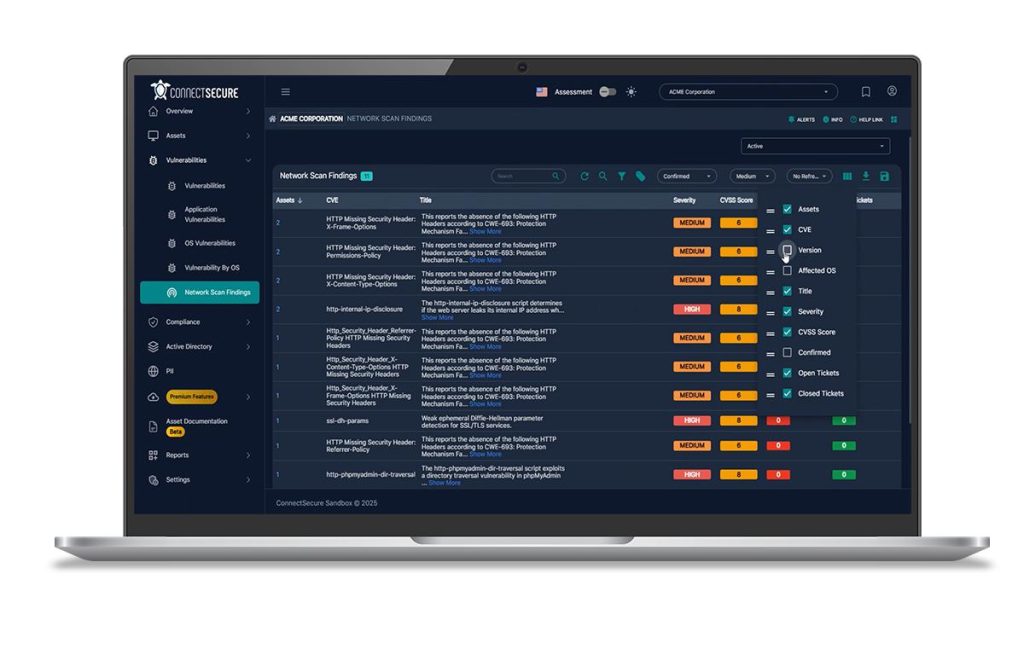
Vulnerability scanning identifies potential security weaknesses, while penetration testing investigates whether selected weaknesses can be exploited and what an attacker could do with them. The two activities support each other, but they answer different questions.
Think of a vulnerability scan as checking a building for unlocked doors, damaged windows, and other possible entry points. A penetration test goes further by checking whether an entry point can actually be used to reach a restricted area. The tester also considers whether several smaller weaknesses can be combined into a more serious attack path.
It’s worth correcting a common misconception: vulnerability scanning isn’t always passive. Some scanners actively probe services, send test requests, or check how an application responds. The main difference is that a standard vulnerability scan generally identifies and classifies potential issues, while a penetration test includes human-led validation and controlled exploitation within an agreed scope.
| Aspect | Penetration testing | Vulnerability scanning |
|---|---|---|
| Main purpose | Determine whether weaknesses can be exploited and assess their impact. | Find and list known or suspected security weaknesses. |
| Typical approach | Manual testing supported by automated tools. | Primarily automated checks, sometimes followed by manual review. |
| Coverage | Usually focused on a defined target and set of objectives. | Can cover a large number of assets on a recurring basis. |
| Results | Validated findings, evidence, attack paths, impact, and remediation advice. | Potential vulnerabilities, affected assets, and recommended fixes. |
| False positives | Findings are investigated, but evidence and interpretation still need review. | May include false positives or issues that need manual validation. |
| Best use | Testing real-world exposure and the effectiveness of security controls. | Finding weaknesses regularly across an environment. |
Most organizations need both. Run vulnerability scans as part of ongoing vulnerability management, then use penetration testing to examine important systems, validate high-risk findings, and uncover weaknesses that automated checks may miss. For a practical overview of tools used in this work, see our guide to free penetration testing tools.
What Are the Main Types of Penetration Testing?
Penetration tests can be grouped by the amount of information the tester receives and by the systems being assessed. Black-box, white-box, and grey-box describe the tester’s starting knowledge. Network, web application, API, cloud, mobile, and wireless testing describe the target.
Black-Box Testing
In a black-box test, the tester receives little or no internal information about the target. The assessment starts from the perspective of an external attacker who may know the organization’s public domain or IP addresses but doesn’t have source code, internal diagrams, or employee credentials.
This approach can show what an outsider can discover from the internet and how far that person might get. It often requires more reconnaissance because the tester must first map the exposed services and application behavior. However, black-box testing doesn’t automatically represent every real attacker. The agreed scope, time limit, and starting conditions still shape the result.
White-Box Testing
In a white-box test, the tester receives substantial information about the target. Depending on the engagement, that may include source code, architecture diagrams, configuration files, test accounts, API specifications, or privileged credentials.
This access can help testers examine logic and trust boundaries that are difficult to assess from the outside. It is useful for a detailed application or internal security assessment, but it doesn’t mean every test includes a complete source-code audit. The contract should state exactly which materials and components are included.
Grey-Box Testing
Grey-box testing gives the tester limited information or a normal user account. For example, a tester may sign in to an online store as a customer and check whether that account can access another customer’s order, change protected account details, or perform actions that should require a higher permission level.
This approach is useful for testing authenticated features and access controls. It can also model the risk of an attacker who has obtained a valid account. The test should make clear which roles and permission levels are being assessed.
Common Penetration Testing Targets
- Network penetration testing: Examines exposed hosts, network services, segmentation, remote access, and weaknesses in internal or external network defenses.
- Web application penetration testing: Tests websites and browser-based applications for issues such as broken access control, authentication flaws, injection, and insecure session handling.
- API penetration testing: Checks API authentication, authorization, object-level access, input validation, rate limits, and unintended data exposure.
- Cloud penetration testing: Reviews permitted cloud assets, identity permissions, exposed services, storage access, network rules, and workload configurations. Testing must follow the cloud provider’s applicable policies.
- Mobile application penetration testing: Examines the mobile app, its local data storage, authentication, communication with backend services, and platform-specific security controls.
- Wireless penetration testing: Assesses Wi-Fi configuration, encryption, authentication, guest network separation, and the risk of unauthorized access.
One engagement may cover more than one target type. A mobile app test, for instance, may need API testing because the app relies on backend services to retrieve and update data.
How Does a Penetration Test Work? A Step-by-Step Process
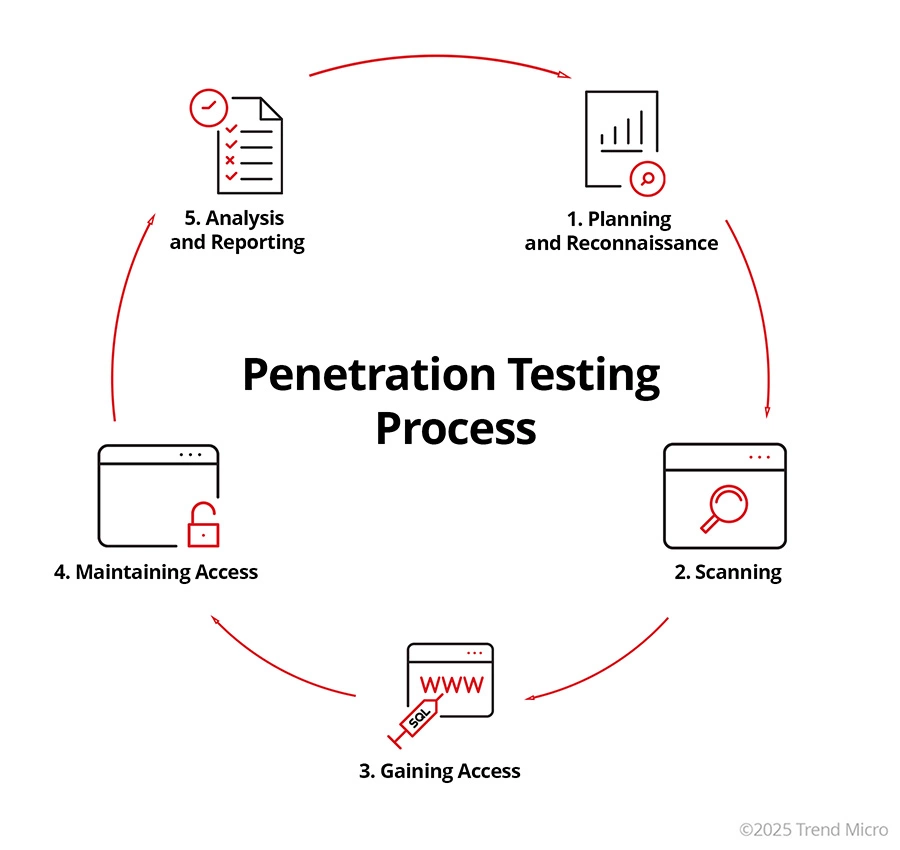
A penetration test follows a planned process, but the exact workflow varies by target and methodology. The phases below reflect common industry practice and are broadly consistent with guidance such as NIST Special Publication 800-115. Not every engagement uses the same phase names, and not every test includes every activity.
1. Define the Scope and Rules of Engagement
Before testing begins, the organization and tester agree on what can be tested, how the work will be performed, and who should be contacted if something goes wrong. This is one of the most important parts of the engagement.
The scope should identify:
- Authorized assets: Domains, IP ranges, applications, APIs, cloud accounts, mobile apps, and environments included in the test.
- Excluded systems: Third-party services, production components, or sensitive systems that must not be tested.
- Testing window: Approved dates and times, including any blackout periods.
- Allowed techniques: Whether social engineering, denial-of-service testing, password attacks, or access to sensitive data are permitted.
- Emergency contacts: People who can pause or stop the test if an unexpected impact occurs.
- Data handling: How evidence is collected, protected, retained, and deleted after the engagement.
Written authorization is essential. If a system is hosted by a third party, the organization should confirm that the planned testing is permitted under the provider’s rules and contracts.
2. Perform Reconnaissance and Map the Attack Surface
Reconnaissance is the information-gathering stage. Depending on the scope, testers may review public DNS records, exposed services, application pages, technology fingerprints, documentation, and other information that helps them understand the target.
Some reconnaissance is passive, meaning it uses information already available without directly interacting with the target. Other methods are active and send requests to systems in scope. The tester records relevant assets and identifies areas that need closer examination.
3. Identify and Validate Potential Weaknesses
Testers use manual checks and tools to examine the target. For a web application, this may include reviewing login and password-reset flows, session behavior, input handling, access permissions, and API requests. For a network test, it may include identifying exposed services, checking configurations, and investigating vulnerable software.
Automated tools can speed up discovery, but their output is not automatically a confirmed vulnerability. Testers need to verify whether a finding is real, whether it is reachable under the test conditions, and whether it creates a meaningful security risk.
4. Attempt Controlled Exploitation
When a potential weakness is found, the tester attempts to validate it using only the techniques allowed by the rules of engagement. The objective is to establish whether the weakness can be exploited and demonstrate its impact with the least intrusive evidence possible.
For example, a tester may use two approved test accounts to check whether one account can access another account’s records. If the access control check fails, the tester can document the request and response while avoiding unnecessary access to real customer information.
Exploitation should stop when the agreed objective has been demonstrated or when continuing would create unacceptable risk. A professional test is not a competition to cause the most damage or extract the most data.
5. Assess Post-Exploitation Impact When Authorized
After gaining a limited foothold, testers may check whether the access can lead to higher privileges, access to other systems, or exposure of sensitive resources. This is often called post-exploitation. It may include privilege escalation or lateral movement, but those activities are not required in every penetration test.
Long-term persistence, destructive actions, data exfiltration, and attempts to hide activity are also not automatic parts of a standard test. They should only be performed when explicitly authorized and when the potential impact has been assessed. In many engagements, a safe proof of access is enough to demonstrate the risk.
6. Document Findings and Deliver the Report
The tester records what was tested, which methods were used, what was found, and what the evidence shows. A useful report connects each technical issue to its practical impact. It should help both technical teams and business leaders understand what needs attention.
Findings commonly include a description, affected asset, severity, evidence, reproduction details, impact, and recommended remediation. Risk ratings may use the Common Vulnerability Scoring System (CVSS), but a CVSS score should not replace business context. A moderate technical issue on a critical business system may deserve faster attention than a higher-scoring issue on an isolated test asset.
7. Remediate and Retest
The organization’s IT, security, or development teams fix the confirmed issues. Fixes may involve patching software, changing permissions, correcting application logic, improving network segmentation, or updating security settings.
Retesting checks whether the specific findings have been fixed. It should also consider whether the change introduced a new problem or whether another path still leads to the same weakness. A retest is not always included in the original quote, so confirm this before signing the engagement.
What Vulnerabilities Can Penetration Testing Find?
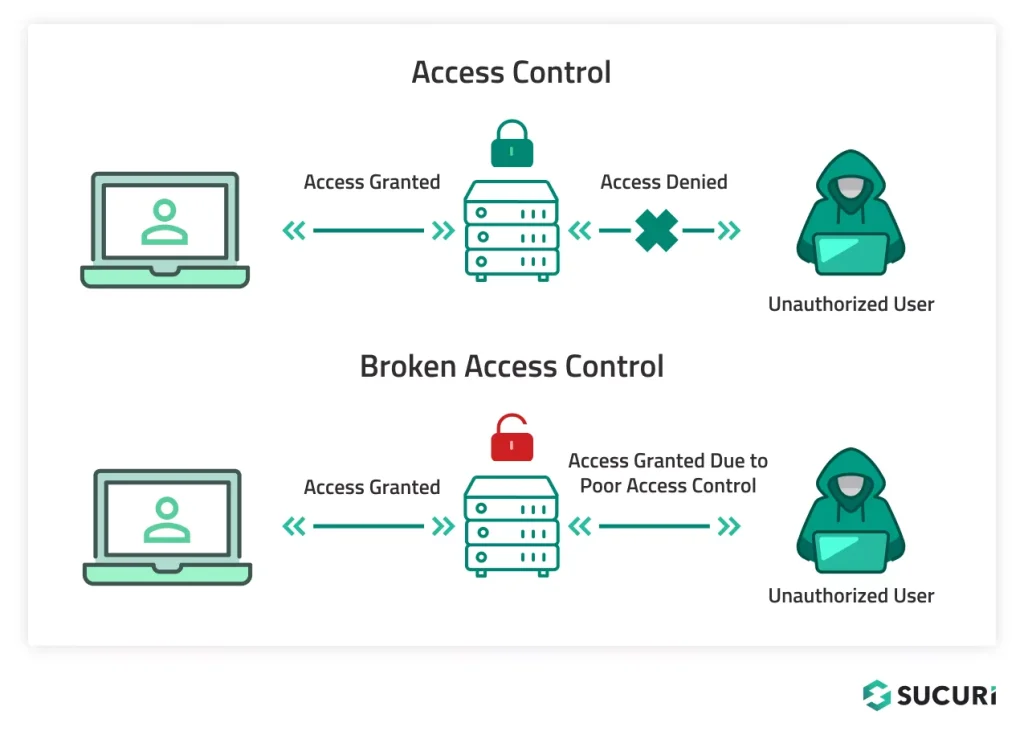
A penetration test can uncover technical flaws, design weaknesses, and configuration problems that expose systems or data. The findings depend on the target, the tester’s access, and the scope of work.
- Broken access control: A user can view or change data or functions that belong to another user or role.
- Authentication weaknesses: Login, password reset, multi-factor authentication, or account recovery flows can be bypassed or abused.
- Injection flaws: Untrusted input changes the way a database, operating system, or application processes a command or query.
- Cross-site scripting (XSS): An application handles untrusted content in a way that allows script execution in another user’s browser.
- Security misconfiguration: Unnecessary services, exposed management interfaces, overly broad permissions, or unsafe defaults increase the attack surface.
- Insecure APIs: API endpoints expose data or actions without proper authorization, validation, or abuse controls.
- Weak network segmentation: A compromised device or account can reach systems that should be isolated.
- Sensitive data exposure: Information is stored, transmitted, or returned in a way that makes unauthorized access more likely.
These examples overlap with topics covered by the OWASP Top 10 and the OWASP API Security Project. Those resources are useful references, but a penetration test should assess the actual application and its business logic rather than simply check off a list.
What Should a Penetration Testing Report Include?
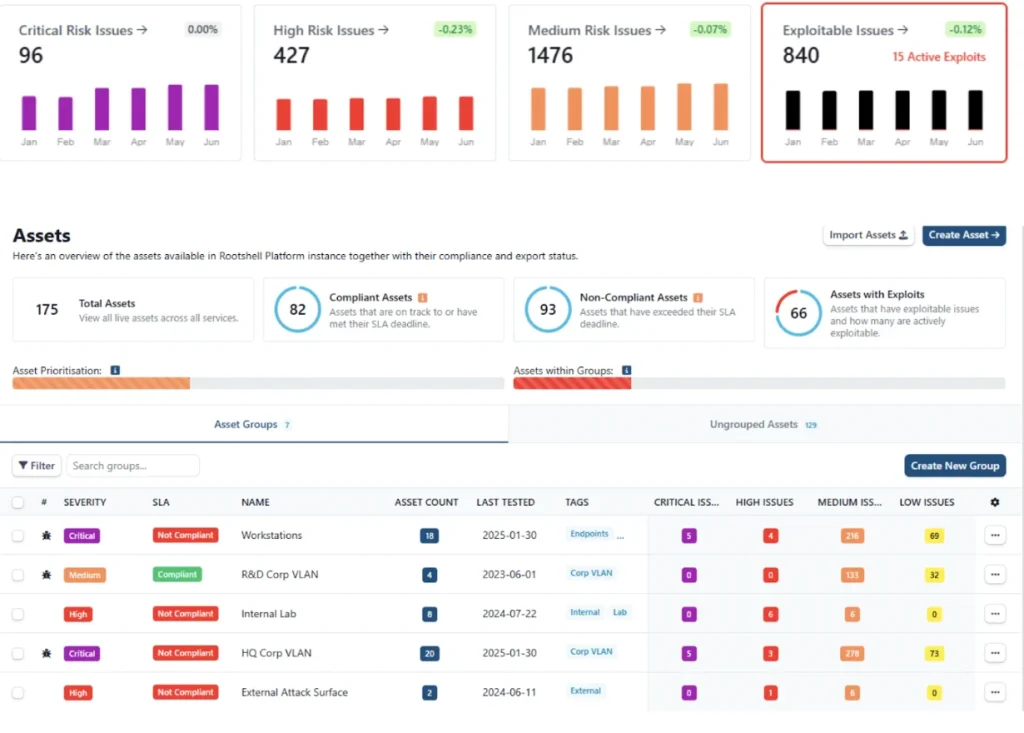
A penetration testing report should do more than list vulnerabilities. It should give decision-makers enough information to understand the risk, assign work, and verify that fixes are effective.
A strong report typically includes:
- Executive summary: A plain-language overview of the scope, main risks, and overall findings.
- Scope and limitations: The systems tested, test dates, exclusions, assumptions, and access provided.
- Methodology: The general approach, tools, and testing standards or guidance used.
- Detailed findings: Each issue’s description, affected asset, severity, evidence, and business impact.
- Proof of concept: Enough technical detail to help the organization reproduce and understand the issue, without exposing unnecessary sensitive data.
- Remediation guidance: Specific fixes or mitigation steps, prioritized by risk.
- Retest results: Which findings were fixed, partially fixed, or remain open after verification.
CVSS can help describe the technical severity of a vulnerability, but it is not a complete business-risk rating. Teams should also consider whether the affected asset is internet-facing, what data it holds, how easy the weakness is to exploit, and what an attacker could do next.
What Are Common Penetration Testing Tools?
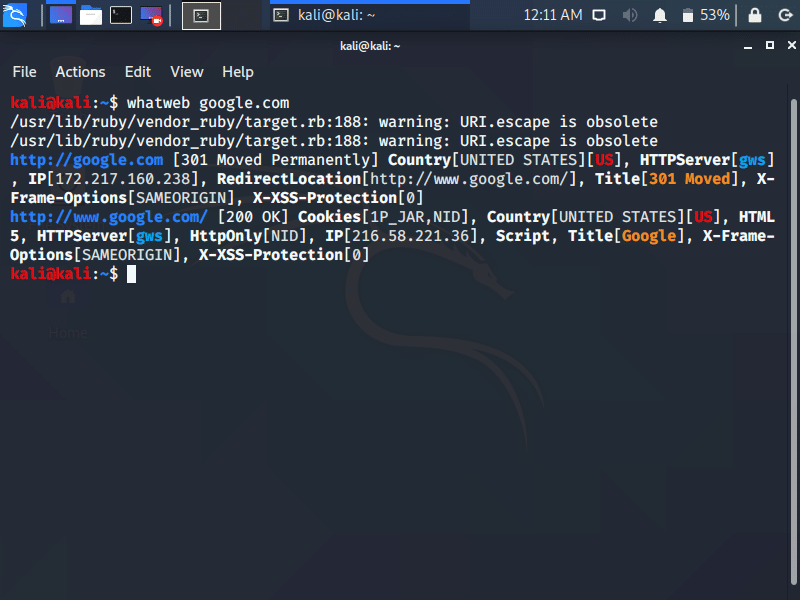
Penetration testers use different tools for network discovery, web application testing, traffic analysis, and controlled exploitation. No single tool can perform a complete assessment. The tester’s judgment, experience, and understanding of the target are just as important.
- Kali Linux: A Linux distribution that packages many security and penetration testing tools. It provides a convenient testing environment; it is not itself a penetration testing method.
- Nmap: A network discovery and port-scanning utility used to identify hosts, open ports, and services. Results need interpretation and should only be collected from authorized targets.
- Burp Suite: A web application testing platform that helps inspect and modify HTTP(S) requests and responses, test input handling, and examine application behavior.
- Metasploit Framework: A framework for developing and running exploit tests. It can help validate known vulnerabilities, but an available exploit does not mean it is safe or appropriate to run against every target.
- Wireshark: A network protocol analyzer used to inspect captured traffic and investigate communication problems or potential information exposure.
- Aircrack-ng: A suite for assessing wireless network security. Its use must be limited to networks for which the tester has explicit permission.
Beginners can use a dedicated lab or intentionally vulnerable practice environment to learn these tools safely. Never scan or test public systems, workplace networks, or someone else’s website without clear authorization.
Why Do Organizations Conduct Penetration Testing?
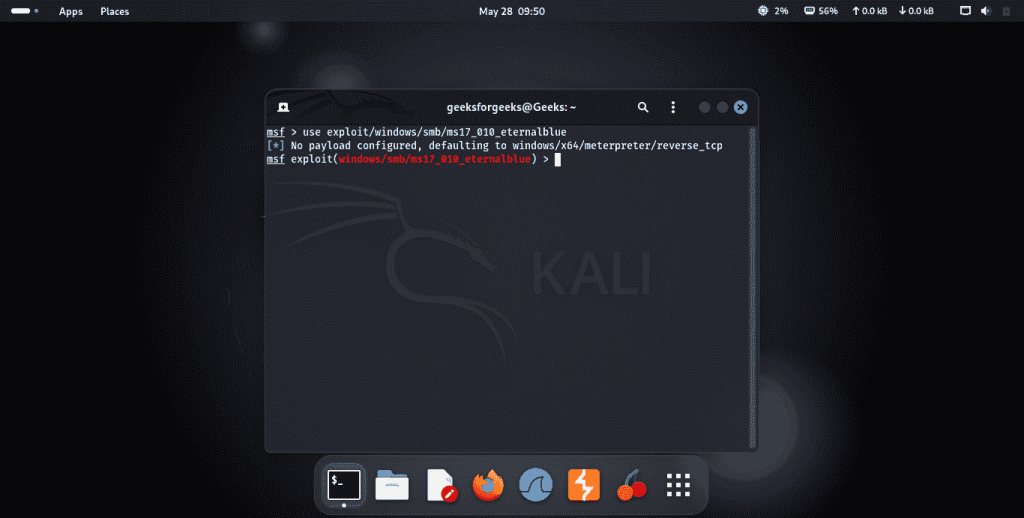
Organizations use penetration testing to understand how weaknesses could affect their systems, customers, and operations. The value comes from turning technical findings into clear decisions about risk and remediation.
- Find exploitable weaknesses: Testing helps distinguish theoretical issues from weaknesses that can be used under the conditions assessed.
- Understand attack paths: A tester may show how several lower-risk issues combine to expose a sensitive system or business process.
- Check security controls: The assessment can reveal whether authentication, access controls, segmentation, and monitoring work as intended.
- Support risk management: Evidence helps teams decide which issues to fix first and where additional safeguards are needed.
- Provide compliance evidence: A properly scoped test may support specific regulatory or contractual requirements, depending on the organization and environment.
- Improve security practices: Findings can help developers, administrators, and security teams understand how design and configuration choices create risk.
Penetration testing can also support broader resilience work, including efforts to protect backup data from ransomware attacks. It should be one part of a security program, alongside patch management, secure development, access reviews, monitoring, backups, and incident response planning.
Does Penetration Testing Help With PCI DSS, GDPR, and ISO 27001?
Penetration testing can provide useful evidence for security and compliance programs, but the requirements differ. It’s inaccurate to say that PCI DSS, GDPR, and ISO 27001 all impose the same universal testing schedule on every organization.
- PCI DSS: The PCI Data Security Standard includes specific penetration testing requirements. Requirement 11.4 addresses penetration testing, including testing after significant changes and defined testing of segmentation where applicable. The exact obligations depend on the applicable PCI DSS version, scope, and assessment context. Organizations should consult the current PCI DSS materials and their qualified assessor.
- GDPR: Article 32 requires organizations to use appropriate technical and organizational measures based on risk. It refers to a process for regularly testing, assessing, and evaluating the effectiveness of security measures. It does not prescribe one universal penetration testing frequency for every controller or processor.
- ISO/IEC 27001: The standard requires an organization to establish and continually improve an information security management system and select risk-based controls. It does not mean every certified organization must perform a penetration test on every system at a fixed interval. Testing may be selected as part of the organization’s risk treatment and assurance activities.
For ISO 27001-related assessments, organizations may work with specialist iso27001 penetration testing services to scope testing around relevant information security risks and controls. The link uses a standard HTML anchor without a nofollow, sponsored, or user-generated-content attribute. A service provider can help with the assessment, but the organization remains responsible for its own ISMS, risk decisions, and compliance evidence.
Penetration Testing vs. Red Teaming: What’s the Difference?
Penetration testing mainly looks for and validates weaknesses within an agreed scope, while red teaming tests whether an organization can detect and respond to a realistic, objective-driven attack. They overlap, but they are not interchangeable.
A penetration test may focus on finding security flaws in a web application or internal network. A red team exercise usually starts with a defined objective, such as accessing a protected business system, and evaluates the organization’s ability to detect, investigate, and respond. It may involve technical attacks as well as approved social engineering or physical security scenarios.
In a red team exercise, the blue team may not know the exact timing or details of the test. That controlled secrecy helps assess detection and response, but it must be agreed upon by authorized leadership and supported by clear safety and escalation procedures. Red teaming is not automatically more mature or better than penetration testing. The right choice depends on the question the organization needs answered.
How Much Does Penetration Testing Cost?
Penetration testing prices vary widely. A small, single-purpose web application assessment is usually less complex than a project covering several applications, internal networks, cloud environments, and mobile platforms. There is no reliable price that applies to every organization or provider.
Ask vendors to explain how the quote relates to the work being performed. Important cost factors include:
- Scope and asset count: The number of applications, APIs, IP addresses, user roles, and environments included.
- Application complexity: Custom workflows, payment features, integrations, and complex authorization rules may require more manual testing.
- Testing approach: Black-box, grey-box, and white-box access can change the time and expertise required.
- Tester experience: Relevant application, cloud, network, or industry experience can matter more than a long list of generic certifications.
- Schedule and delivery: Short deadlines, after-hours work, on-site requirements, and formal reporting needs can affect the quote.
- Retesting: Confirm whether one retest is included, how soon it must be requested, and whether additional testing costs extra.
Before comparing prices, make sure each provider is quoting for the same scope and deliverables. A low-cost scan marketed as a penetration test is not equivalent to a manual assessment with validated findings, a clear report, and retesting.
How Often Should You Perform a Penetration Test?
There is no single testing schedule that fits every organization. Frequency should reflect the risk of the systems, how often they change, contractual or regulatory obligations, and the results of previous assessments.
Consider a new test or a focused reassessment when:
- A major application, API, network, or cloud environment is launched.
- Significant changes are made to infrastructure, authentication, access controls, or application architecture.
- A system begins processing more sensitive data or supporting a more critical business function.
- A serious vulnerability or security incident reveals a gap that needs deeper investigation.
- A regulation, customer contract, or internal risk policy requires testing at a defined interval.
- Previous findings have been fixed and need independent verification.
Many organizations schedule periodic testing and add assessments after significant changes. Continuous vulnerability monitoring can help identify new issues between engagements, but it does not replace a manual penetration test when one is needed.
How Do You Choose a Penetration Testing Provider?
The right provider should understand your technology and business risks, explain the proposed test clearly, and deliver findings your team can act on. Don’t choose a vendor based only on a certification list or the number of tools it uses.
Before signing, ask these questions:
- Have you tested systems like ours? Ask for relevant experience with your application stack, cloud platform, industry, or network environment.
- What exactly is in scope? Request a written list of assets, user roles, exclusions, test windows, and allowed techniques.
- How do you validate findings? Ask how the team distinguishes confirmed vulnerabilities from scanner output and how it avoids unnecessary access to sensitive data.
- What will the report contain? Confirm that it includes evidence, impact, severity, remediation advice, and an executive summary.
- Is retesting included? Clarify the number of retests, deadlines, and any additional fees.
- How do you protect our information? Discuss confidentiality, evidence storage, access to test data, retention, and secure deletion.
- How will you handle an incident? Agree on emergency contacts, stop conditions, and notification procedures before testing starts.
A provider should be comfortable explaining limitations as well as capabilities. Be cautious of promises that a test will find every vulnerability, guarantee compliance, or make an organization completely secure.
What Are the Current Trends in Penetration Testing?
Penetration testing is adapting as organizations rely more on cloud services, APIs, software delivery pipelines, and AI-enabled applications. These changes affect what needs to be tested and how often security teams reassess their environments.
- AI-assisted testing: AI tools can help summarize information, generate test ideas, and speed up parts of analysis. Their output still needs human review. AI-generated results can be incorrect, incomplete, or unsafe to run without checking.
- API security: APIs connect mobile apps, websites, and business services. Testing increasingly needs to examine authorization at the object and function level, not just whether an endpoint requires a login.
- Cloud and container security: Cloud identity permissions, exposed services, workload configuration, and container deployment choices can create paths into sensitive environments. Testing must stay within provider policies and customer authorization.
- Continuous security validation: Some organizations combine recurring automated checks with periodic human-led testing. These services can provide more frequent feedback, but the term “continuous penetration testing” can describe different levels of automation and manual involvement. Buyers should check what is actually delivered.
- Business logic testing: Testers are paying close attention to flaws in workflows, roles, transactions, and application-specific rules. These issues can be difficult for generic scanners to understand.
These are practical shifts in testing priorities, not a guarantee that every organization needs every new tool or service. The most useful approach is to test the systems and workflows that matter to the organization’s real risk profile.
Frequently Asked Questions About Penetration Testing
Is penetration testing legal?
Yes, penetration testing is legal when the tester has explicit authorization from the owner or an authorized operator of the systems being tested. Get permission in writing and define the scope, timing, allowed techniques, and emergency contacts. Testing systems without permission can violate laws, contracts, or acceptable-use policies.
Can penetration testing damage a system?
It can. Even a carefully planned test carries some risk, especially when it involves production systems, fragile services, authentication changes, or active exploitation. A professional team reduces that risk through scoping, safe test methods, monitoring, and stop conditions. Discuss potentially disruptive techniques before the engagement and decide whether they should be excluded or tested in a non-production environment.
Is a vulnerability scan enough?
Not in every situation. Vulnerability scanning is useful for recurring checks and broad asset coverage, but it may not uncover business logic flaws, complex access control problems, or attack paths that require manual investigation. Penetration testing adds deeper validation. The two methods are complementary.
Does a small business need penetration testing?
It depends on the business’s systems, data, exposure, and risk. A small company that handles customer information, online payments, or business-critical applications may benefit from a focused test. A smaller scope can make the assessment more manageable. Start with the systems that would cause the greatest harm if compromised.
Can I perform a penetration test myself?
You can learn security testing in a lab or assess systems you own and are authorized to test. However, a self-assessment may miss issues because you already know how the system is intended to work. An independent tester can provide a different perspective and may be required by a contract or compliance program. Don’t test third-party systems without permission.
Does a penetration test guarantee that my organization is secure?
No. A penetration test is limited by its scope, time, access, and methods. It provides evidence about the systems and conditions tested, not a guarantee that every weakness has been found. Security needs ongoing maintenance, monitoring, patching, access control, backups, and incident response planning.
Conclusion: Use Penetration Testing to Make Better Security Decisions
Penetration testing helps organizations see how real weaknesses could affect their systems and data. Its value isn’t measured by the number of vulnerabilities in a report. A useful assessment explains which issues are exploitable, what an attacker could reach, how serious the impact may be, and what the organization should do next.
Start with a clear scope, written authorization, and a testing approach that matches the systems and risks you need to assess. Use vulnerability scanning for recurring discovery, bring in qualified testers for deeper validation, and make sure the engagement includes a practical report and a plan for retesting fixes.
No single test can prove that an organization is completely secure. But a well-scoped penetration test can turn uncertainty into evidence and help teams spend time and resources on the weaknesses that matter most.
You May Also Like
 Data Security & Privacy
Tokenization vs Encryption: Key Differences and Best Practices
 Data Security & Privacy
How Encryption Works: A Practical Guide to Data Encryption Best Practices
 Cybersecurity
Why Strong Passwords Are Important?
 Data Security & Privacy
Endpoint Security vs Antivirus: Key Differences for Better Protection
 Network Security
11 Best Free Penetration Testing Tools: Your Complete Guide for 2027
 Cybersecurity
What Is Endpoint Management? A Practical Guide for Modern Teams
 Data Security & Privacy
The Importance of Vulnerability Management and Attack Surface Management
 Cybersecurity
Effective Strategies for Prioritizing Cybersecurity Vulnerability Remediation
 Web Development
