

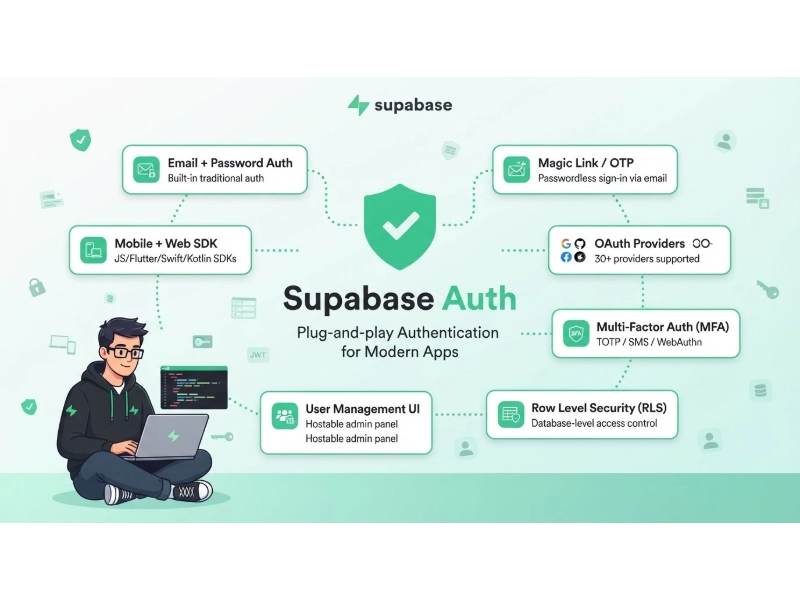
Supabase Auth is a managed authentication service for adding email login, passwordless authentication, social login, phone verification, multi-factor authentication, and enterprise single sign-on to web and mobile applications.
Its most important advantage is its direct relationship with PostgreSQL. After Supabase verifies a user’s identity, your application can use JSON Web Tokens and Postgres Row Level Security policies to determine which database rows that user can read, create, update, or delete.
This makes Supabase Auth especially useful for applications that need authentication, database authorization, APIs, file storage, serverless functions, and real-time features under one platform. If you are still comparing backend platforms, see our guide to the best Backend-as-a-Service providers and our detailed Supabase vs. Firebase comparison.
However, Supabase does not automatically make an application secure. A production implementation still requires tested Row Level Security policies, protected server credentials, carefully configured redirect URLs, production-ready email or SMS delivery, abuse prevention, and deliberate session management.
Supabase Auth at a Glance
| Capability | Supabase Auth support |
|---|---|
| Email and password | Yes |
| Magic links | Yes |
| Email OTP | Yes |
| Phone OTP | Yes, with a supported SMS provider |
| Social login | Yes, including Google, Apple, GitHub, Microsoft, and others |
| Anonymous sign-in | Yes |
| Enterprise SSO | SAML 2.0 on eligible paid plans |
| Multi-factor authentication | TOTP and phone-based factors |
| Session management | JWT access tokens and rotating refresh tokens |
| Database authorization | PostgreSQL Row Level Security |
| Custom roles and claims | JWT claims and Auth Hooks |
| Custom email and SMS delivery | SMTP, messaging providers, and Auth Hooks |
| Self-hosting | Available, with additional operational responsibility |
| Client libraries | JavaScript, Flutter, Swift, Kotlin, Python, and other environments |
Is Supabase Auth Right for Your Application?
Supabase Auth is often a strong choice when an application already uses—or plans to use—Supabase Postgres, Storage, Realtime, Edge Functions, or its generated Data API.
It can also operate as a standalone identity service, but its greatest practical value usually comes from the connection between:
- User authentication
- JWT-based sessions
- PostgreSQL authorization
- Row Level Security
- Supabase APIs, Storage, and Edge Functions
Supabase Auth verifies identity, but it does not automatically understand every application’s permission model. Developers remain responsible for defining ownership rules, roles, tenant boundaries, privileged actions, and account-recovery procedures.
What Is Supabase Auth?
Supabase Auth is the authentication component of the Supabase development platform. It provides API endpoints and client libraries for registering users, verifying identities, issuing sessions, managing accounts, and integrating external identity providers.
Supported authentication methods include:
- Email and password
- Magic links
- Email one-time passwords
- Phone and SMS verification
- Social login
- Anonymous sign-in
- Multi-factor authentication
- SAML 2.0 enterprise SSO
Supabase Auth uses an authentication service based on GoTrue and stores identity information in a dedicated auth schema inside the project’s PostgreSQL database. This managed schema contains users, identities, sessions, refresh tokens, MFA factors, and other authentication records.
Application-specific profile data generally belongs in a separate table, such as public.profiles, rather than being written directly to auth.users. A profile table can reference the authenticated user’s UUID and be protected by Row Level Security.
For a broader explanation of where authentication fits into an application stack, see our guide to back-end infrastructure.
What Supabase Auth manages
Supabase can manage:
- User registration and sign-in
- Email and phone verification
- Password recovery
- Social identity providers
- Access and refresh tokens
- Active user sessions
- MFA enrollment and verification
- SAML identity-provider connections
- Authentication audit information
- Authentication email and SMS workflows
- Identity linking for eligible non-SSO identities
What developers still need to manage
Your application is generally responsible for:
- Designing roles and permissions
- Writing and testing RLS policies
- Protecting server-side secret keys
- Configuring allowed redirect URLs
- Setting up production SMTP and SMS delivery
- Preventing account enumeration and automated abuse
- Designing account recovery
- Deciding when MFA is required
- Managing OAuth provider tokens when calling provider APIs
- Monitoring failed logins and unusual account behavior
- Meeting applicable privacy and compliance requirements
Supabase reduces the amount of authentication infrastructure a team must build, but it does not remove the need for a complete identity and access-management model.
Authentication and Authorization
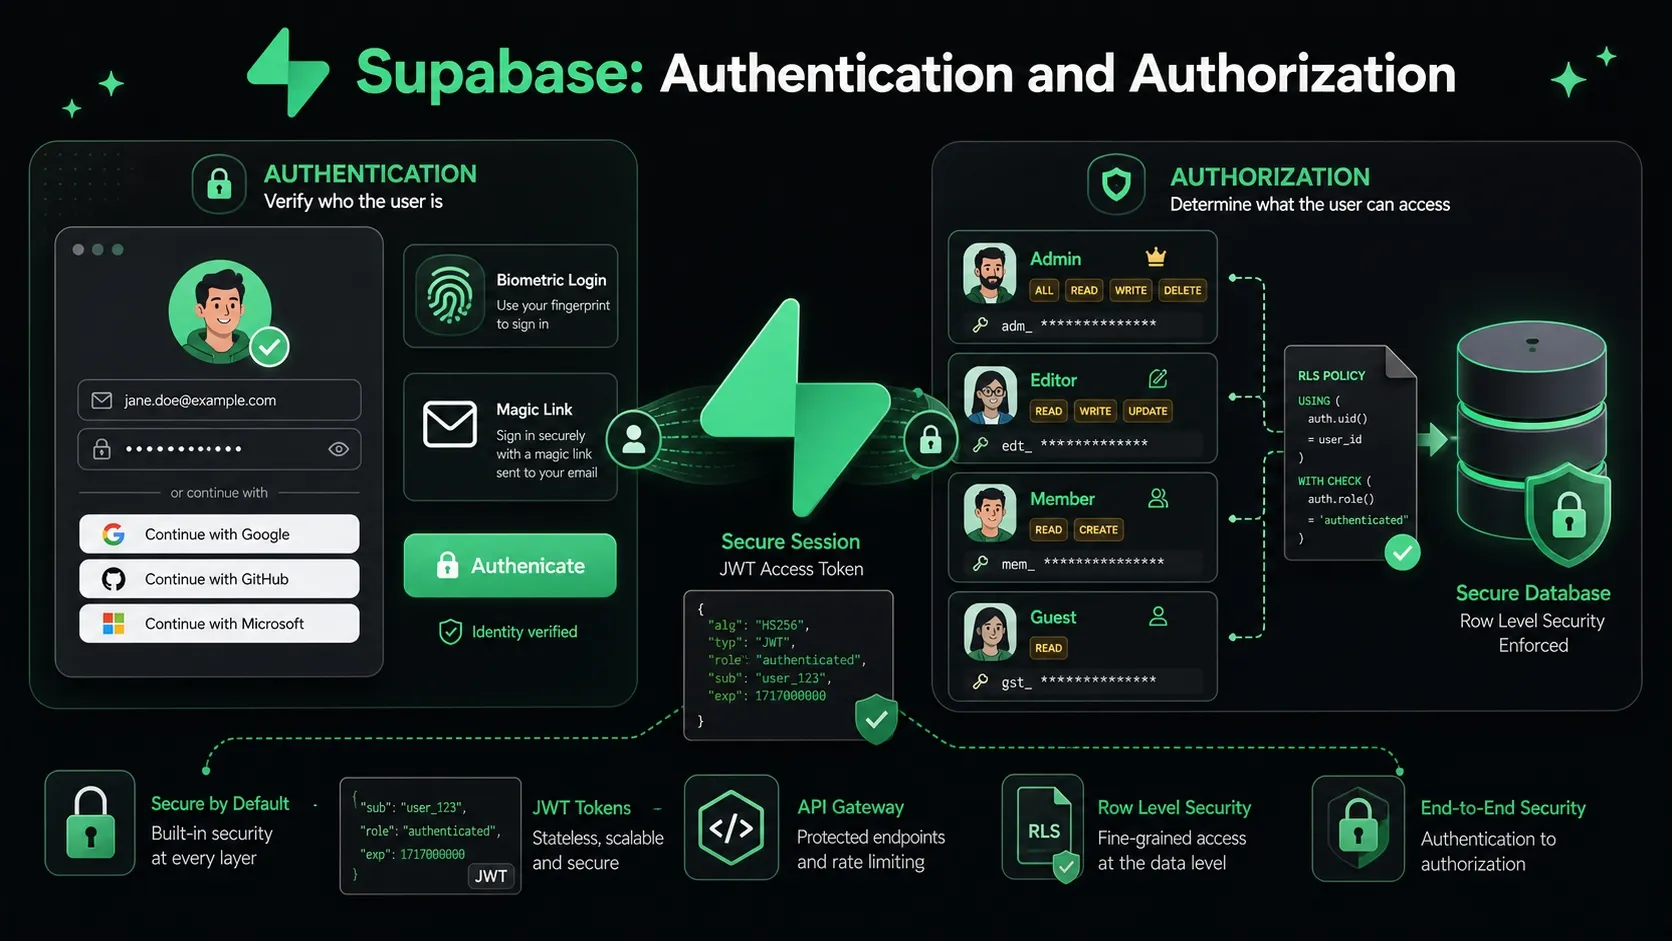
Authentication and authorization are related, but they solve different problems:
- Authentication determines who the user is.
- Authorization determines what the user is allowed to access or change.
Supabase Auth handles authentication through passwords, OAuth providers, OTPs, SSO, and MFA. Authorization is commonly implemented through PostgreSQL grants, Row Level Security policies, JWT claims, and server-side application checks.
For a deeper comparison of permission models, read our guide to ABAC vs. RBAC.
How authentication works
A typical Supabase authentication flow looks like this:
- A user signs in with a password, OTP, social provider, or SSO connection.
- Supabase verifies the supplied credentials or identity-provider response.
- Supabase creates an authenticated session.
- The application receives an access token and refresh token.
- The access token identifies the user when the application calls Supabase services.
- PostgreSQL evaluates grants and RLS policies before returning or changing data.
The access token is a JSON Web Token containing claims about the authenticated user and session.
How authorization works
Supabase maps API requests to PostgreSQL roles:
anonrepresents requests without a signed-in user.authenticatedrepresents requests with a valid user session.service_roleis a privileged server-side role that bypasses RLS.
The service_role key—or the corresponding newer secret key—must never be embedded in a browser, public mobile application, client-side bundle, public repository, or other untrusted environment.
For browser and mobile applications, database authorization should normally be enforced through RLS.
Row Level Security
Postgres Row Level Security allows the database to determine which rows a request may access.
For example, this policy permits authenticated users to read only profile records associated with their own Supabase user ID:
create policy "Users can read their own profile"
on public.profiles
for select
to authenticated
using ((select auth.uid()) = user_id);
The policy effectively adds an authorization condition to every applicable query.
A secure RLS implementation should account for:
SELECTINSERTUPDATEDELETE- Anonymous visitors
- Authenticated users
- Ownership changes
- Organization membership
- Administrative operations
- Multi-tenant isolation
RLS should be enabled on every table exposed through the Supabase Data API unless the table is intentionally public and protected by another appropriate design.
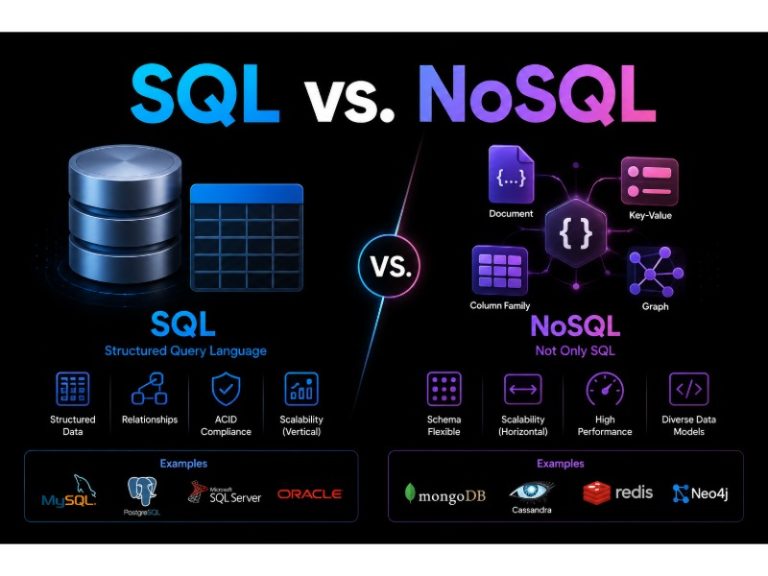
Database structure also affects authorization design. Our SQL vs. NoSQL guide explains when relational tables, foreign keys, constraints, and document-oriented data models are appropriate.
Database grants and RLS policies
PostgreSQL grants and RLS policies perform different jobs:
- Grants determine whether a database role may perform an operation at all.
- RLS policies determine which rows that operation may affect.
A table should not retain unnecessary privileges simply because an RLS policy exists. Apply least privilege at both levels.
User metadata versus app metadata
Supabase exposes metadata through JWT claims, but the metadata location matters:
user_metadatamay be updated by the authenticated user and should not be trusted for authorization.app_metadatacannot normally be edited directly by the user and is more appropriate for trusted roles, plans, and organization claims.
Even trusted JWT claims can become temporarily stale until Supabase issues a new access token. For permissions that must change immediately, consider checking the current database state rather than relying only on an existing token.
Supabase Ecosystem
Supabase Auth can operate independently, but it is designed to work with the broader Supabase ecosystem.
Supabase Postgres
Authentication records are stored in the project’s PostgreSQL database under the managed auth schema. Application tables can reference auth.users.id, giving each user a stable UUID.
Common application tables include:
- Profiles
- Organizations
- Team memberships
- Roles
- Subscriptions
- Projects
- Documents
- Audit events
Avoid using an email address as the permanent relational identifier for a user. Email addresses can change, and SSO configurations can result in separate identities with the same email value. A user UUID is generally a safer reference.
Supabase Data API
Supabase can expose eligible PostgreSQL objects through its generated Data API. When a signed-in client sends an access token, Postgres can evaluate the user’s identity and claims through RLS.
This allows many applications to query the database from a browser without creating a custom API endpoint for every operation. It does not mean database security can be skipped.
Client-side checks improve user experience, but they are not a reliable security boundary. RLS and server-side authorization must enforce access even when someone calls an API directly.
Supabase Storage
Supabase Storage can use the same authenticated user session and RLS model to control file access.
Storage policies can restrict uploads and downloads according to:
- User ID
- Storage bucket
- Object path
- Organization membership
- Account role
- Subscription status
For example, an application can isolate uploads under object paths associated with each authenticated user’s UUID.
Supabase Edge Functions
Edge Functions can receive Supabase access tokens and apply authenticated server-side logic. They are commonly used for:
- Payment workflows
- Signed webhooks
- Privileged database operations
- Transactional email
- Calling external APIs
- Generating signed resources
- Applying custom business rules
Secret keys used for privileged operations must remain inside the server-side function environment.
Supabase Realtime
Supabase Realtime works alongside Postgres and RLS. Authenticated clients can receive database changes, broadcast messages, and presence updates according to the application’s configuration and access policies.
Building applications with Supabase
Supabase works with frameworks and environments such as:
- Next.js
- React
- Vue
- Nuxt
- SvelteKit
- Flutter
- Swift
- Kotlin
- React Native
- Python
- Node.js
Developers using AI-assisted application builders can also read our practical guide to building apps with Lovable and Supabase. Security-sensitive output should still be reviewed manually, particularly database migrations, RLS policies, server credentials, and redirect configuration.
Server-rendered frameworks typically use cookie-based session handling and PKCE. Follow the latest Supabase SSR documentation for your framework instead of relying on outdated authentication-helper packages.
Supabase Authentication Methods
| Method | Best suited for | Main consideration |
|---|---|---|
| Email and password | Familiar account-based applications | Requires password reset and email verification workflows |
| Magic link | Low-friction email login | Depends on access to the user’s email account |
| Email OTP | Passwordless, cross-device login | Requires reliable email delivery |
| Phone OTP | Mobile-first or phone-identified users | Introduces SMS cost and abuse risks |
| Social login | Faster onboarding | Requires provider and redirect configuration |
| SAML SSO | Business and enterprise customers | Requires an eligible paid plan |
| Anonymous sign-in | Guest carts, games, and onboarding | Requires identity-upgrade and cleanup strategies |
| MFA | Sensitive accounts and operations | Must be enforced through authorization |
No single authentication method is ideal for every application. Many products combine several methods—for example, email login for individual customers, Google login for convenience, SAML SSO for enterprise tenants, and MFA for administrators.
Social Auth / OAuth2
Supabase Social Login lets users authenticate through an external identity provider.
Common supported providers include:
- Apple
- Azure or Microsoft
- Bitbucket
- Discord
- Figma
- GitHub
- GitLab
- Kakao
- Keycloak
- Notion
- Slack
- Spotify
- Twitch
- WorkOS
- X or Twitter
- Zoom
The exact provider list and configuration requirements can change. Verify the provider-specific guide before implementing production login.
OAuth 2.0 and OpenID Connect
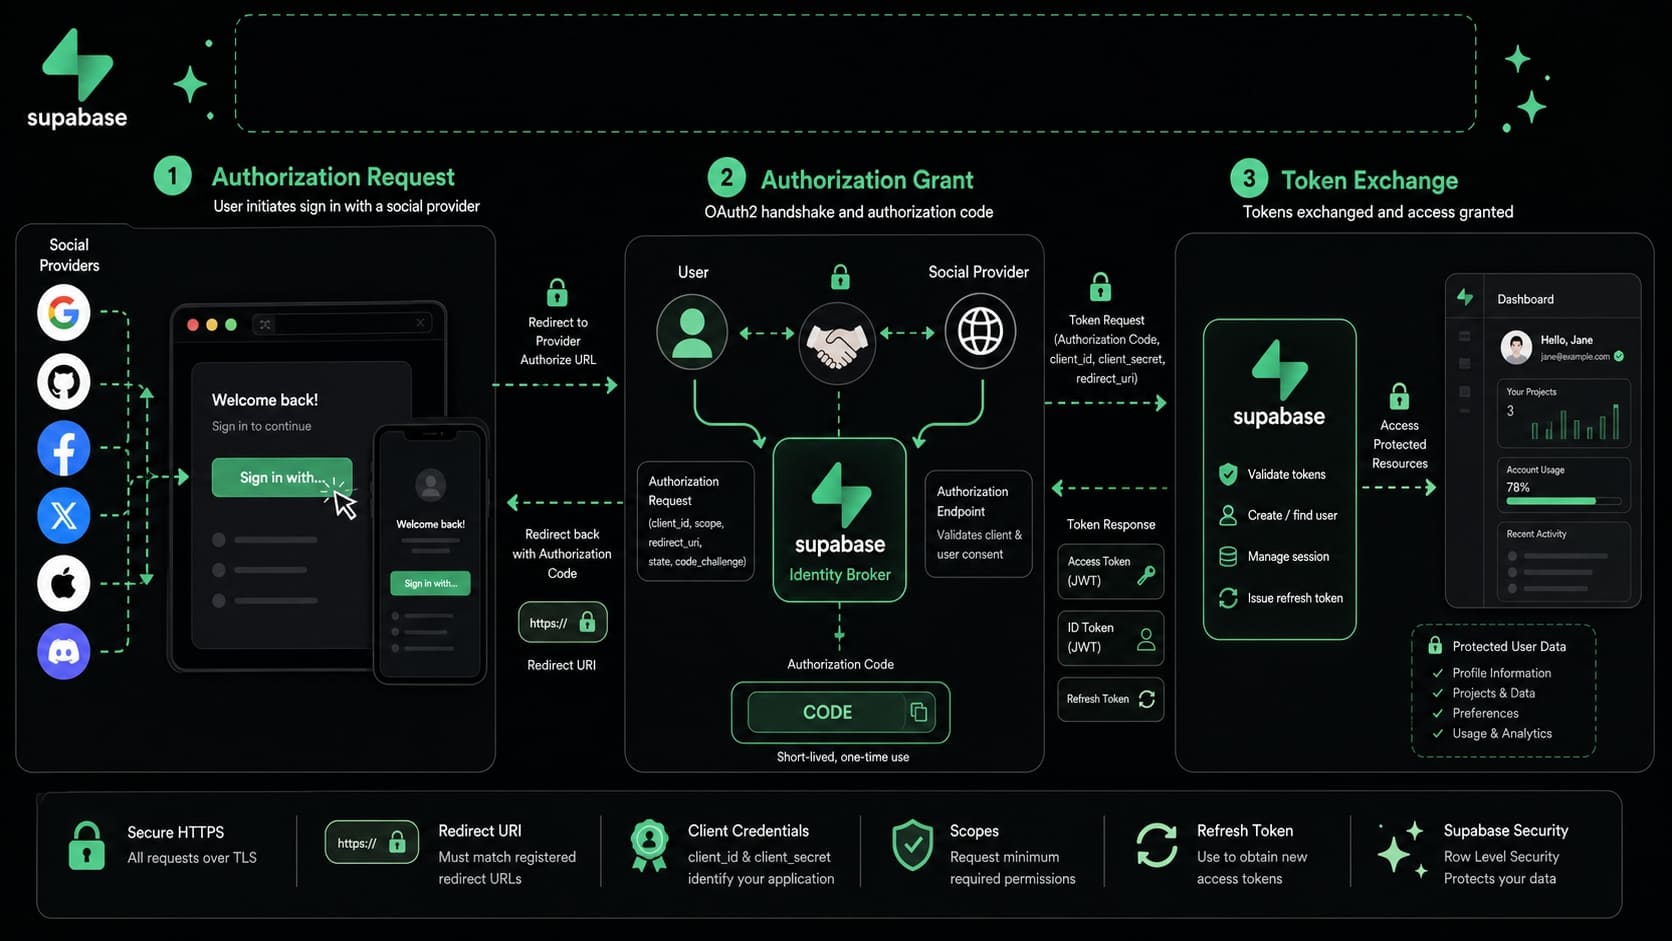
OAuth 2.0 is primarily an authorization framework. Identity providers commonly combine it with OpenID Connect or provider-specific identity APIs so an application can determine who signed in.
A typical Supabase social-login flow works like this:
- The application redirects the user to an identity provider.
- The provider authenticates the user.
- The provider redirects the user to Supabase.
- Supabase validates and processes the provider response.
- Supabase redirects the user to an approved application URL.
- The application establishes a Supabase session.
Social login should not be confused with Supabase’s separate OAuth 2.1 authorization-server capability. Social login lets users authenticate to your application through another provider, while an OAuth authorization server lets third-party applications request authorized access to your product.
Redirect URLs
OAuth redirect configuration is one of the most common sources of authentication errors.
Configure:
- The correct Supabase callback URL in the provider dashboard
- The application Site URL in Supabase
- Approved local-development redirect URLs
- Preview-environment URLs when required
- Production callback URLs
- HTTPS for production environments
Use the narrowest practical redirect allow list. Overly broad wildcard rules can create open-redirect risks or send authentication responses to unintended locations.
PKCE
Proof Key for Code Exchange, or PKCE, is typically appropriate for server-rendered applications, mobile apps, and environments where an authorization code must be exchanged securely for a session.
Use current Supabase SSR libraries and framework-specific guidance for cookie handling. Older authentication tutorials may no longer represent the recommended approach.
OAuth provider tokens
A Supabase access token and an OAuth provider token serve different purposes:
- The Supabase token authorizes requests to your Supabase application.
- The provider token authorizes calls to services such as Google, GitHub, or Microsoft.
Supabase does not automatically refresh social-provider tokens for your application. If the product needs ongoing access to a provider’s API, securely store and refresh provider credentials according to that provider’s requirements.
Never expose long-lived provider refresh tokens in browser storage, analytics systems, error reports, or application logs.
Supabase Phone Auth
Supabase Phone Auth provides passwordless authentication through a one-time code sent by SMS or WhatsApp, depending on the supported provider and configured channel.
Documented provider integrations include:
- Twilio
- Vonage
- MessageBird
- TextLocal as a community-supported option
Provider availability may vary based on deployment type, region, and current Supabase configuration.
How phone login works
A standard phone-login flow is:
- The user enters a phone number.
- Supabase requests an OTP from the configured messaging provider.
- The provider delivers the code.
- The user enters the received code.
- The application sends the phone number and code to Supabase.
- Supabase verifies the code and creates a session.
Users signing in through phone OTP do not need to create a password.
Benefits of phone authentication
Phone authentication can be useful for:
- Mobile-first applications
- Delivery and transportation services
- Marketplaces
- Appointment systems
- Applications where email use is uncommon
- Verifying that a user can receive messages at a number
Limitations and risks
Phone authentication is not automatically more secure than every password-based flow. Teams should consider:
- SMS delivery charges
- Country-specific regulations
- Message delays or failures
- Unsupported destinations
- Phone-number recycling
- SIM-swap attacks
- Automated OTP abuse
- Shared phone numbers
- Account recovery when a number changes
Use CAPTCHA or another anti-bot control where appropriate, apply rate limits, and monitor unusual sending patterns. Messaging-provider charges are generally separate from the Supabase subscription.
Supabase OTP
A one-time password is a temporary code used to verify possession of an email inbox, phone number, or enrolled authentication factor.
Supabase supports several OTP-related experiences:
- Email OTP
- Phone OTP
- Magic links
- Phone-based MFA codes
- Authenticator-app TOTP
Although these methods all involve temporary credentials, they do not provide identical security properties or user experiences.
Email OTP
With email OTP, a user receives a six-digit code and enters it in the application.
By default, calling the sign-in-with-OTP method for an email address sends a magic link. To send a numeric email OTP instead, customize the relevant email template to include the token variable.
New users may be created automatically during an OTP flow unless the application disables automatic account creation using the appropriate client option.
Magic links
A magic link lets a user authenticate by clicking a single-use link delivered by email.
Magic links can reduce password-reset support, but they still require:
- Reliable email delivery
- Correct Site URL configuration
- Approved redirect URLs
- Secure email templates
- Short-lived, one-time links
- Protection against unintended redirects
- A clear confirmation experience
OTP expiration and resend behavior
According to the current Supabase documentation, email magic links and OTPs generally have a default expiration of one hour and a default resend interval of 60 seconds.
The Auth rate-limit documentation currently lists:
- A default project-wide limit of 30 OTP requests per hour
- A default 60-second interval before another OTP request for the same user
- Additional verification limits based on IP address
Project owners should confirm these values under Authentication → Rate Limits.
For a broader explanation of request quotas, token buckets, abuse controls, and HTTP 429 responses, read our guide to API rate limiting.
Production email delivery
The built-in Supabase email provider is intended primarily for evaluation and has restrictive delivery limits. Current documentation lists a limit of two authentication emails per hour through the built-in provider.
Production applications should generally configure a custom SMTP service and set up:
- A verified sender identity
- SPF
- DKIM
- DMARC
- Bounce handling
- Rate limits
- Branded templates
- Delivery monitoring
- Alerting
A custom SMTP provider gives the application more control, but it does not guarantee inbox placement. Domain reputation and email configuration still matter.
SSO
Supabase supports enterprise Single Sign-On using SAML 2.0 on eligible paid plans.
Compatible identity providers include:
- Microsoft Entra ID
- Okta
- Google Workspace
- OneLogin
- PingIdentity
- Auth0
- Other SAML 2.0-compatible identity providers
Supabase acts as the SAML Service Provider, while the customer’s identity platform acts as the Identity Provider.
When SSO is useful
SAML SSO is commonly requested by:
- B2B SaaS customers
- Enterprise organizations
- Universities
- Government institutions
- Healthcare organizations
- Companies with centralized employee identity management
SSO can simplify employee onboarding and offboarding because access is controlled through the customer’s identity provider.
Multi-tenant SSO
Supabase can support multiple SAML connections within one application. Each connection receives an identity-provider identifier that can be used in JWT claims and authorization policies.
This allows a SaaS platform to associate each SSO provider with an organization or tenant. Authorization should verify the organization relationship rather than trusting an email domain alone.
Important SSO behavior
Supabase documentation identifies several important behaviors:
- SAML users are not automatically linked to existing password or social-login users.
- An SSO identity and a regular identity can create separate accounts with the same email address.
- Applications should reference users by UUID instead of assuming email uniqueness.
- The identity provider may impose its own maximum session duration.
- SAML assertions must include an email address Supabase can recognize.
- Single Logout support is limited, making session timeouts important for forced reauthentication.
SSO is not the same as social OAuth. Social login usually helps individual users sign in with personal accounts, while SAML SSO connects an application to an organization’s identity directory.
User Sessions
A Supabase user session begins after successful authentication.
Each session is represented by:
- A short-lived JWT access token
- A rotating refresh token
- A session record in
auth.sessions
The access token accompanies API requests. The refresh token is exchanged for a new access-token and refresh-token pair when the access token needs to be renewed.
Default session behavior
By default:
- Sessions can remain active until a terminating event occurs.
- A user can maintain sessions on multiple devices.
- Access tokens are short-lived.
- Refresh tokens are intended for one-time use, with limited reuse handling for legitimate race conditions.
Supabase recommends the default one-hour access-token lifetime for most applications and generally discourages extremely short expirations. Very short JWT lifetimes increase refresh traffic and can create issues with clock skew and long-running requests.
Session controls
Eligible paid plans provide controls such as:
- Maximum session lifetime
- Inactivity timeout
- Single session per user
- Configurable JWT expiration
- Sign-out scope
- Refresh-token reuse detection
Changes to session controls are usually evaluated during a token refresh. They may not invalidate every existing access token immediately.
Signing out and token validity
Deleting a session does not necessarily invalidate an already issued JWT at the exact same moment. The access token may remain valid until its expiration unless a sensitive endpoint also verifies whether the corresponding session_id remains active.
For many applications, short-lived access tokens provide a reasonable balance. Sensitive actions may require:
- A current server-side session check
- Password confirmation
- A new MFA challenge
- A recently authenticated session
Secure session practices
Recommended practices include:
- Use official Supabase libraries for session refresh.
- Use PKCE and current SSR libraries for server-rendered applications.
- Avoid placing tokens in URLs.
- Never log access or refresh tokens.
- Use appropriate
Secure,SameSite, and cookie-path settings. - Protect the application from cross-site scripting.
- Reauthenticate before sensitive account changes.
- Let users terminate other sessions where appropriate.
- Avoid treating a decoded JWT as automatically trustworthy.
Server-side code should verify JWT signatures and validate relevant claims, including the issuer, audience, and expiration.
MFA
Multi-factor authentication adds another verification step after the initial login.
Supabase supports:
- Time-based one-time passwords through authenticator applications
- Phone-based MFA codes
Authenticator-app TOTP is part of basic MFA functionality, while phone-based advanced MFA has separate pricing on eligible paid projects.
Authenticator Assurance Levels
Supabase adds an Authenticator Assurance Level to the user’s JWT:
aal1indicates conventional authentication, such as a password, magic link, OTP, phone login, or social login.aal2indicates that the user also completed a second-factor challenge.
Applications can use the aal claim in:
- Frontend navigation
- Backend API checks
- Edge Functions
- RLS policies
- Sensitive-action verification
MFA must be enforced
Displaying an MFA form does not enforce MFA by itself. The application must deny protected operations when the required assurance level is missing.
A product can require MFA:
- For every user
- For administrators
- For specific organizations
- For users who enrolled in MFA
- Before changing billing information
- Before changing security settings
- Before accessing regulated data
Database policies can require aal2 for sensitive operations. This reduces the risk that someone can bypass a frontend check by calling an API directly.
MFA recovery
A complete MFA implementation should include a recovery strategy, such as:
- Backup codes
- Multiple enrolled factors
- Verified recovery channels
- Support-assisted recovery
- Identity-verification procedures
- Administrative audit logs
- Notifications when factors are added or removed
Recovery should not be so weak that it defeats the protection provided by MFA.
Auth Hooks
Supabase Auth Hooks allow applications to add custom behavior at specific points in the authentication lifecycle.
A hook can be implemented as:
- A PostgreSQL function
- An HTTP endpoint
Postgres Hooks run within the database environment. HTTP Hooks can integrate with external systems but introduce network latency and availability considerations.
Available Auth Hooks
| Auth Hook | Typical use | Current plan availability |
|---|---|---|
| Before User Created | Validate or reject a registration | Free and Pro |
| Custom Access Token | Add or modify JWT claims | Free and Pro |
| Send SMS | Customize SMS content or delivery | Free and Pro |
| Send Email | Customize email delivery | Free and Pro |
| MFA Verification Attempt | Apply additional MFA controls | Team and Enterprise |
| Password Verification Attempt | Control password-verification attempts | Team and Enterprise |
Plan availability can change, so verify the current Auth Hooks and pricing documentation.
Before User Created Hook
This hook runs before Supabase creates a user. It can:
- Restrict registration to an approved domain
- Block disposable email addresses
- Enforce invitation-only registration
- Validate account metadata
- Apply tenant-specific onboarding requirements
Avoid returning unnecessarily detailed rejection messages, since they can assist account enumeration.
Custom Access Token Hook
The Custom Access Token Hook runs before Supabase issues a JWT. It can add trusted claims such as:
- Application role
- Organization ID
- Subscription tier
- Feature entitlement
- Tenant membership
Keep claims compact because the JWT is sent with requests. Claim changes usually do not appear inside an existing access token until the token is refreshed.
Send Email and Send SMS Hooks
Delivery hooks can route authentication messages through custom communication services.
Possible uses include:
- Transactional email providers
- Regional SMS providers
- Localized authentication messages
- Custom branding
- Centralized delivery logging
- Provider failover
Never log OTP values, magic-link tokens, authorization codes, access tokens, or refresh tokens.
Hook security and reliability
Auth Hooks are part of the authentication path. A slow or unavailable hook can stop users from signing in.
Supabase currently documents execution windows of approximately:
- Two seconds for Postgres Hooks
- Five seconds for HTTP Hooks
Keep hook logic focused and observable. Apply minimal database permissions and restrict function execution to the required Supabase Auth role.
Supabase recommends explicit permissions rather than broadly privileged security definer functions. If a security-definer function is necessary, pin its search_path, schema-qualify database objects, and review its privileges carefully.
Pricing
Supabase pricing combines an organization subscription with project compute and variable usage. Authentication costs are mainly influenced by monthly active users, third-party users, SSO users, phone MFA, email delivery, SMS delivery, and related infrastructure usage.
The figures below reflect the official Supabase pricing page and billing documentation reviewed on September 1, 2026.
| Authentication item | Free | Pro and Team | Enterprise |
|---|---|---|---|
| Monthly active users | 50,000 included | 100,000 included, then $0.00325 per MAU | Custom |
| Third-party MAU | 50,000 included | 100,000 included, then $0.00325 per MAU | Custom |
| SAML SSO MAU | Not available | 50 included, then $0.015 per SSO MAU | Custom |
| Basic MFA | Included | Included | Included |
| Advanced phone MFA | Not included | Paid add-on | Custom |
| Social OAuth providers | Included | Included | Included |
| Custom SMTP | Supported | Supported | Supported |
| Single session per user | Not included | Included | Included |
| Configurable session timeouts | Not included | Included | Included |
| Auth audit-log retention | One hour | Seven days on Pro; 28 days on Team | Plan-specific |
| Auth Hooks | Selected hooks | Availability depends on plan | All |
For a wider breakdown of subscription fees, compute, database storage, file storage, and overage costs, see our Supabase pricing guide. Always use the official pricing page as the final source of truth.
Advanced MFA phone pricing
Current documentation lists Advanced MFA Phone at approximately:
- $0.1027 per hour, or about $75 per month, for the first enabled project
- About $10 per month for each additional enabled project
Messaging-provider charges may also apply.
What counts as an MAU?
A monthly active user is generally a unique user who performs an authenticated activity during the billing period.
Supabase separately tracks:
- Standard MAU
- Third-party MAU
- SSO MAU
Review the current billing definitions when forecasting costs, especially if the application combines standard authentication, third-party JWTs, and enterprise SSO.
Other costs to consider
Authentication can create expenses beyond the base MAU calculation:
- Custom SMTP delivery
- SMS or WhatsApp messages
- Database compute
- Database storage
- Edge Function invocations
- Network egress
- Log drains
- Custom domains
- Advanced MFA
- Additional projects
- Monitoring services
The Free plan can be appropriate for prototypes and smaller projects, but a production budget should account for the entire architecture rather than authentication MAU alone.
Supabase Auth Security Best Practices
Use this checklist before deploying Supabase Auth to production:
- Enable RLS on every exposed table.
- Configure database grants as well as RLS policies.
- Write policies for reading, inserting, updating, and deleting.
- Test both allowed and denied operations.
- Never expose a secret or
service_rolekey to a client. - Store trusted roles in
app_metadata, not user-editable metadata. - Use UUIDs instead of email addresses as permanent user references.
- Configure a production SMTP provider.
- Configure SPF, DKIM, and DMARC.
- Restrict OAuth redirect URLs.
- Use HTTPS in production.
- Use PKCE for appropriate SSR and mobile flows.
- Avoid storing tokens in URLs or logs.
- Add CAPTCHA or equivalent abuse protection.
- Monitor email and SMS consumption.
- Apply reasonable authentication rate limits.
- Require MFA for privileged users.
- Enforce MFA through APIs or RLS.
- Create a secure account-recovery process.
- Review active-session and timeout requirements.
- Rotate exposed credentials immediately.
- Keep Supabase SDKs updated.
- Review authentication and provider logs after unusual activity.
- Minimize the personal data collected during registration.
Authentication is only one part of protecting user information. For broader security and privacy planning, see our guides on how companies can protect customer data and data protection and privacy.
Advantages and Limitations
Advantages
- Direct integration with PostgreSQL
- RLS-based database authorization
- Password and passwordless login options
- Social login and SAML SSO
- Managed JWT and refresh-token sessions
- TOTP and phone-based MFA
- Customizable Auth Hooks
- SDKs for major web and mobile platforms
- Open-source components
- A self-hosting option
- Shared identity across Database, Storage, Realtime, and Edge Functions
Limitations
- Secure RLS design requires PostgreSQL knowledge.
- The built-in email provider is unsuitable for normal production volume.
- Phone authentication requires an external messaging provider.
- SMS authentication introduces delivery costs and abuse risks.
- Some session controls, SSO features, hooks, and phone MFA require paid plans.
- OAuth provider-token refresh remains the application’s responsibility.
- JWT claims can remain stale until a new token is issued.
- Self-hosting transfers maintenance and security responsibilities to your team.
- SSO identities are not automatically linked with existing regular accounts.
- A misconfigured RLS policy can expose sensitive application data.
When Should You Use Supabase Auth?
Supabase Auth is often a good fit when:
- The application already uses Supabase Postgres.
- You want database-level authorization through RLS.
- A frontend needs direct but controlled access to application data.
- You need email, social, OTP, phone, and enterprise login methods.
- Authentication must integrate with Storage and Edge Functions.
- Your team is comfortable reviewing SQL policies.
- You want managed authentication with a possible self-hosting path.
- Your data model is relational or multi-tenant.
Consider a specialized identity platform when the project requires highly advanced identity governance, extensive directory synchronization, complex machine-to-machine authorization, deeply customized enterprise federation, or compliance capabilities not included in the selected Supabase plan.
The appropriate choice depends on the entire identity and access-management model—not only the appearance of the login page.
Frequently Asked Questions
Is Supabase Auth free?
Supabase includes Auth on its Free plan, with 50,000 monthly active users included according to the current pricing page. SAML SSO, advanced phone MFA, longer audit retention, advanced session controls, and certain hooks require eligible paid plans or add-ons.
Does Supabase Auth support Google login?
Yes. Supabase supports Google and several other social identity providers. You must create provider credentials, configure the Supabase callback URL, enable the provider, and approve application redirect URLs.
Does Supabase Auth support OAuth 2.0?
Yes. Supabase supports OAuth-based social login. It also offers a separate OAuth 2.1 server capability for applications that need Supabase to act as an authorization server. These are related but different use cases.
Does Supabase Auth support phone numbers?
Yes. Supabase Phone Auth can send OTP codes through supported messaging providers. You need to configure a provider, manage delivery costs, and protect the authentication endpoint against automated abuse.
What is the difference between a magic link and an email OTP?
A magic link authenticates a user when they click a one-time email link. An email OTP requires the user to enter a temporary numeric code. Both are passwordless methods, but the interaction and cross-device experience differ.
Does Supabase support MFA?
Yes. Supabase supports authenticator-app TOTP and phone-based MFA. The application must implement enrollment, challenge, verification, enforcement, and recovery. Phone MFA is an advanced paid capability.
Does Supabase support SSO?
Yes. Supabase supports SAML 2.0 enterprise SSO on eligible paid plans. It can connect to providers such as Okta, Microsoft Entra ID, Google Workspace, and other SAML-compatible systems.
How does Supabase authorization work?
Supabase commonly uses PostgreSQL grants and Row Level Security policies. The user’s JWT supplies identity and session claims, while database policies determine which rows and operations are permitted.
Are Supabase sessions stored in cookies?
Supabase sessions consist of access and refresh tokens. Server-rendered browser applications commonly store session information in cookies through supported Supabase SSR patterns. The appropriate storage approach depends on the framework and whether client-side JavaScript needs access to the session.
Is the Supabase anon key safe to expose?
The publishable key, or legacy anonymous key, is intended for client use. However, it does not secure the database by itself. RLS policies and database grants must protect exposed data. Secret and service_role keys must remain server-side.
Can Supabase Auth be self-hosted?
Yes. Self-hosting is available, but your team becomes responsible for upgrades, availability, secrets, database maintenance, SMTP, SMS integration, OAuth configuration, monitoring, backups, and security.
Is Supabase Auth better than Firebase Authentication?
Neither is universally better. Supabase Auth is especially attractive for PostgreSQL applications that benefit from RLS. Firebase Authentication can be a stronger fit for applications already using Firebase’s mobile SDKs, Firestore, Analytics, Crashlytics, or Google Cloud services. See our full Supabase vs. Firebase comparison for the broader architectural differences.
Final Verdict
Supabase Auth is more than a hosted sign-in form. It is an identity layer designed to connect authenticated users with PostgreSQL, Row Level Security, APIs, Storage, Realtime, and Edge Functions.
Its strongest use case is an application that benefits from database-native authorization. Email login, passwordless authentication, phone OTP, social OAuth, MFA, Auth Hooks, and SAML SSO provide broad identity coverage, while RLS can enforce permissions close to the underlying data.
That flexibility also creates responsibility. A secure Supabase implementation depends on tested RLS policies, protected server credentials, reliable email and SMS infrastructure, restricted redirect URLs, thoughtful session controls, enforced MFA, abuse protection, and a defensible recovery process.
For teams comfortable with PostgreSQL and the wider Supabase ecosystem, Supabase Auth can provide a practical balance of developer experience, customization, and granular data access control.
You May Also Like
 Web Development
Building Apps with Lovable and Supabase: A Step-by-Step Guide
 Web Development
15 Best CyberPanel Alternatives in 2026: Free and Paid
 Web Development
Heroku vs. Netlify (2026): Pricing, Features, and Best Uses
 Cloud Computing
8 Best AWS S3 Alternatives Compared: Pricing, Egress, and S3 Compatibility
 Web Development
Supabase vs Firebase: Which Backend Platform is Right for Your Project?
 Mobile App Development
10 Best Backend as a Service Providers In 2026 for Your Business
 Web Development
REST API vs SOAP API: Differences, Pros & Cons, and Use Cases
 Web Development
What Is API Rate Limiting? (A Practical, Simple Guide for Safer, Faster APIs)
 Web Development
