


Strong passwords matter because weak, reused, or stolen passwords are one of the easiest ways for attackers to take over accounts. A password that is long, random, and unique pushes automated guessing, credential stuffing, and offline cracking so far out of reach that, for practical purposes, they stop being viable attacks.
There’s important context, though. In its 2026 Data Breach Investigations Report, which analyzed incidents from November 2024 through October 2025, Verizon found that exploiting software vulnerabilities overtook stolen credentials as the most common way attackers break in — the first time in the report’s 19-year history that credentials lost the top spot. Stolen credentials are still a leading entry point, and most organizations and individuals will never patch their way out of a reused-password problem. It’s also true that a strong password can’t stop phishing, which tricks you into handing over a perfectly good password. That’s why the main US guidance sources — the National Institute of Standards and Technology (NIST), the Cybersecurity and Infrastructure Security Agency (CISA), and the Federal Trade Commission (FTC) — all pair password advice with a recommendation to turn on multi-factor authentication (MFA).
This article explains what makes a password strong, how attackers actually break passwords, what current official guidance says, and the practical steps — password managers, passphrases, breached-password checks, and passkeys — that make strong passwords realistic instead of a memory burden.
What Makes a Password Strong?
Security agencies define a strong password by three properties, not by how clever it looks. CISA sums it up as long, random, and unique.
- Long: at least 16 characters (more is better).
- Random: a mix of upper- and lowercase letters, numbers, and symbols — or a passphrase of 5–7 unrelated words.
- Unique: used for only one account.
Each property defeats a different kind of attack, which is why all three matter together.
Length Beats Complexity
For years, many sites forced passwords like P@ssw0rd1! a capital letter, a number, a symbol, and only eight characters. Those rules are now considered outdated. NIST, whose Digital Identity Guidelines are the most widely cited password standard in the United States, tells verifiers not to impose composition rules (requiring mixtures of character types).
The reason is mathematical. Adding characters expands the number of possible passwords exponentially; adding a required symbol adds almost nothing, because attackers know exactly which substitutions people make. A 16-character random password is astronomically harder to guess than a “complex” 8-character one. Length is the property that does the real work.
Randomness Defeats Guessing
Predictable passwords fail quickly even when they’re long. Password-cracking tools don’t guess letter by letter at random; they try dictionaries, previously breached passwords, and common human patterns first — names of pets, sports teams, keyboard walks likeqwertyuiop, and year-appended variations. The National Cybersecurity Alliance’s annual Oh, Behave! survey, cited by CISA, found that 35% of people still use personal details like pet names or family members in their passwords, rising to 52% among Gen Z respondents. Randomness — whether from a password generator or a truly unrelated word chain — is what removes those patterns.
Uniqueness Limits Blast Radius
Uniqueness is the property most people underestimate. Data breaches happen constantly, and when a site is breached, its password file (or a decrypted copy) often ends up online. If you reuse that password, one company’s breach becomes your breach everywhere. Attackers run automated credential stuffing campaigns that try leaked email-and-password pairs against banks, email providers, shopping sites, and social networks at massive scale. CISA’s consumer guidance tells the story of a woman whose bank was nearly emptied because she reused one password across her email and bank accounts — the password had already appeared in a breach posted online.
Here’s a hypothetical — and very ordinary — chain of events. An online store you ordered from two years ago gets breached. The store’s password file surfaces in a criminal forum, and a bot spends the next few weeks testing your email-and-password pair against banking, email, and social sites. If the password was reused, the breach follows you into those accounts. If it was unique, the damage stops at the store — an inconvenience rather than a cascading problem.
A unique password for every account means a breach at one service is far more likely to stay contained there.
How Attackers Actually Break Passwords
“Strong” only makes sense relative to the attacks it must survive. There are four main ways passwords get beaten, and they call for different defenses.
| Attack type | How it works | What defeats it |
|---|---|---|
| Credential stuffing | Automated replay of leaked username/password pairs from other sites’ breaches | Unique passwords per account; breached-password screening; MFA |
| Offline cracking | Attacker steals a site’s password file and guesses at full speed on their own hardware | Long, random passwords; sites using slow, salted password hashing |
| Online guessing / dictionary attacks | Repeated login attempts against a live site using common words and patterns | Long, random passwords; the site’s rate limiting (NIST caps consecutive failures at 100) |
| Phishing and social engineering | Trick you into entering your password on a fake site or sharing it directly | MFA (ideally phishing-resistant); passkeys; user awareness |
Two points are worth pausing on. First, offline cracking is where raw length pays off: once an attacker has a stolen password file, how fast they can guess is limited mainly by their hardware and by how quickly the site’s hashing runs, so the password itself becomes the main barrier. Second, a strong password won’t stop phishing, because phishing doesn’t break the password — it collects it from you. That limitation is exactly why NIST requires multi-factor authentication at its higher assurance levels and why the FTC advises that even strong passwords are vulnerable, making two-factor authentication an important additional step.
What Official Guidance Says
If your mental model of password rules comes from workplace policies written a decade ago, current guidance will look different. Here’s what the primary sources actually require or recommend.
| Guidance | Source | What it says |
|---|---|---|
| 15-character minimum for single-factor passwords; 8-character minimum when paired with MFA | NIST SP 800-63B (Digital Identity Guidelines, Aug 2025 edition) | Normative requirements for verifiers |
| Allow at least 64 characters; accept spaces and all printable characters | NIST SP 800-63B | Makes long passphrases practical |
| No composition rules, no password hints, no security questions | NIST SP 800-63B | Complexity theater is out |
| Screen new passwords against blocklists of breached, common, and context-specific passwords | NIST SP 800-63B | Entire password is compared, not substrings |
| No periodic password changes unless there’s evidence of compromise | NIST SP 800-63B | Rotation without cause degrades password quality |
| At least 16 characters, random, unique; passphrase of 5–7 unrelated words as an alternative | CISA | Consumer and small-business recommendation |
| Use a password manager; enable MFA, especially on email, financial, and social accounts | CISA and FTC | Reduces memory burden and residual risk |
The NIST guidance is worth reading closely, because it reverses several rules people were taught as best practice. NIST requires verifiers to check proposed passwords against a blocklist that includes passwords from previous breach corpuses, dictionary words, and context-specific words such as the service name or the username — and to reject blocked passwords with an explanation. It also prohibits forcing periodic expiration: changing passwords on a schedule pushes people toward predictable patterns like Winter2026!, so NIST says a forced change should happen only when there’s evidence a password was compromised. Finally, NIST requires rate limiting — no more than 100 consecutive failed attempts on a single account before the authenticator is disabled — because online guessing is already constrained when sites do their job.
For everyday users, the practical translation is simple: make it long, make it random, make it unique, check it against breaches, add MFA, and stop rotating on a calendar.
Why Length Matters Most
An honest way to see why length matters is to compare how long different passwords take to crack offline. The table below is illustrative, not a measurement. It assumes a password drawn randomly from the 95 printable ASCII characters, and two attack speeds: a fast offline attack against a weakly stored password file (an unsalted MD5- or SHA-1-class hash) at 100 billion guesses per second on modern cracking hardware, and a slow attack against a properly protected file (a bcrypt-class salted hash) at 10,000 guesses per second. Real-world results vary with the site’s hashing, the attacker’s hardware, and whether the password is random at all.
| Password length | Entropy (bits) | Worst-case time, fast offline attack | Worst-case time, slow salted hash |
|---|---|---|---|
| 8 characters | ~53 | ~18 hours | ~21,000 years |
| 12 characters | ~79 | ~171,000 years | ~1.7 trillion years |
| 16 characters | ~105 | ~14 trillion years | ~1.4 × 10²⁰ years |
Three caveats keep this honest. The figures describe worst-case exhaustive search of a random password — a real 8-character password like monkey12 falls in seconds because it’s on cracking dictionaries, while a 16-character random string is safe for any practical purpose. The speeds are assumptions that show the general shape of the math, not benchmark results from a specific attack. And none of this protects a password that an attacker simply steals through phishing or malware — which is the gap MFA and passkeys address.
The overall pattern holds regardless: each added character multiplies the search space, so going from 8 to 16 characters buys you far more than any symbol-for-letter substitution ever will.
How to Create and Manage Strong Passwords in Practice
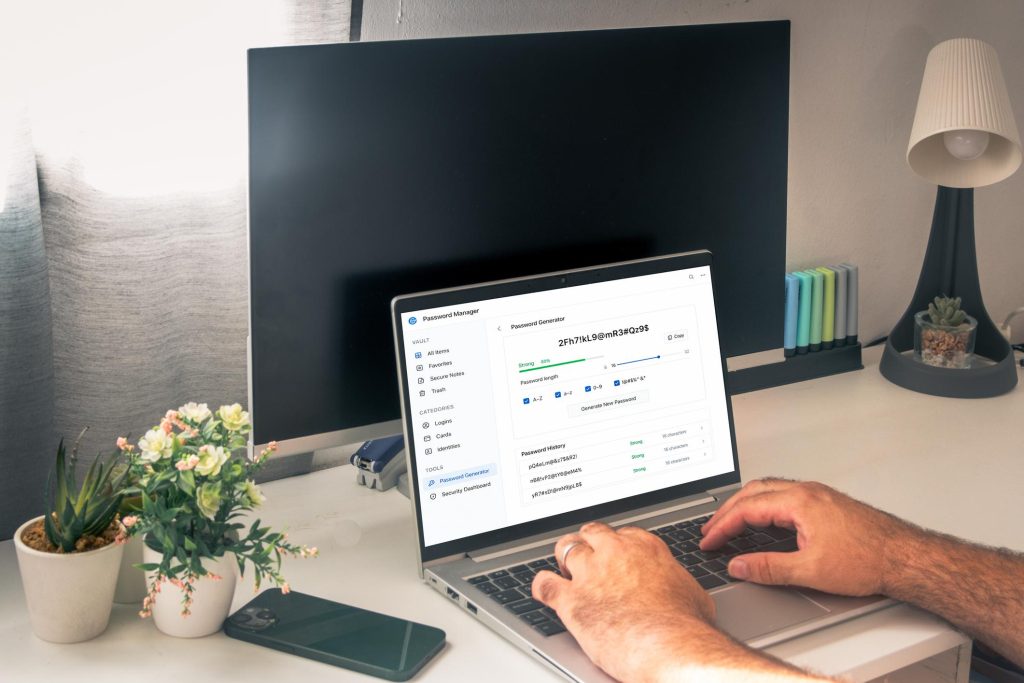
Knowing the rules is easy; living with dozens of 16-character random secrets isn’t — unless you let software do the remembering. Here’s a practical sequence.
- Get a password manager. CISA is direct about this: for most people, generating and remembering long, random, unique passwords for every account isn’t possible, so use a password manager to generate, store, and auto-fill them. Options include the managers built into major browsers and operating systems (many free) and standalone products — Consumer Reports and similar trusted reviewers are a reasonable way to compare them.
- Set a strong master password you can actually remember. A passphrase of 5–7 unrelated words — something like
copper-lantern-drifts-past-granite— meets the length requirement and is far easier to memorize than a symbol-studded short password. Make sure the words are unrelated; a famous quote or song lyric is a dictionary attack magnet. - Replace your weakest and most reused passwords first. Start with accounts whose compromise hurts most: primary email, banking, healthcare, tax, and social accounts. Your email account deserves special priority because whoever controls it can usually reset the passwords on everything else.
- Change any password that has appeared in a breach. You can check individual passwords against the Pwned Passwords corpus maintained by security researcher Troy Hunt. The service uses a k-anonymity model: your password is hashed locally in your browser, and only the first five characters of the hash are sent to the service, so the full password and its complete hash are never transmitted. Many password managers run the same check automatically. Note the service’s own honest caveat: not appearing in the corpus doesn’t prove a password is good — it only means it isn’t known to have been breached.
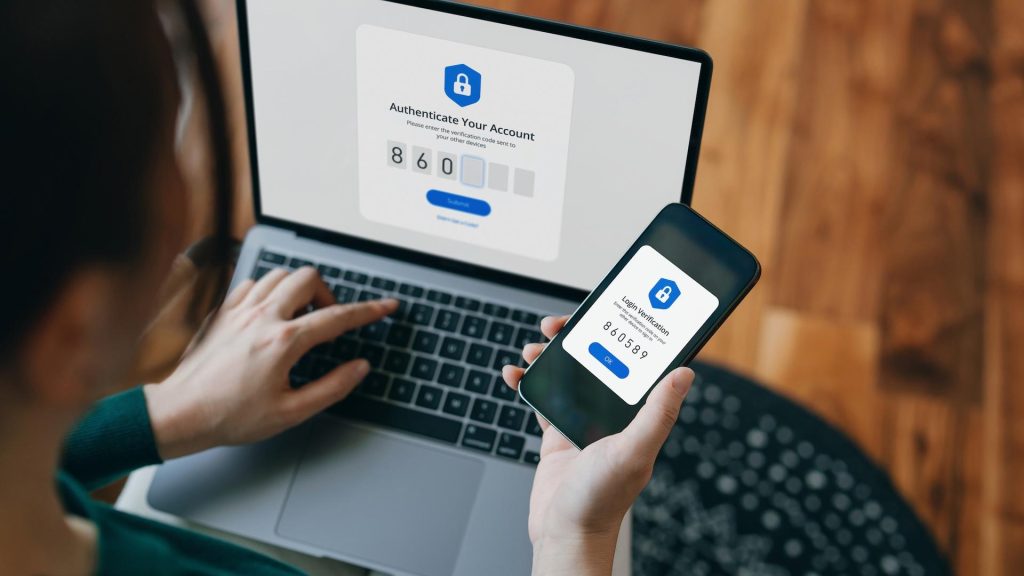
- Turn on MFA everywhere it’s offered. CISA recommends enabling it especially for email, social media, and financial accounts. The FTC notes that one-time passcodes sent by text or email are the least secure two-factor option and suggests an authenticator app or security key where you have the choice. Where available, passkeys (covered below) fold this protection into the login itself.
- Change default passwords on devices and equipment. CISA warns that many products ship with default credentials that are printed on the device or published online, and tells businesses to require changing them before use. Routers, cameras, and smart-home gear are common offenders.
If you’re doing this for a household or small organization, expect the transition to take a couple of focused sessions — the password manager does most of the work once it’s in place.
Common Mistakes That Undermine Strong Passwords
These are the failure patterns that show up most often, each of which quietly cancels the strength of an otherwise good password.
- Reusing a strong password everywhere. Strength doesn’t fix the reuse problem. Credential stuffing works against a strong password just as well as a weak one if it’s been leaked — the password doesn’t have to be cracked.
- Patterned “unique” passwords.
BlueTulip2026for email andRedTulip2026for the bank isn’t uniqueness as attackers model it; cracking tools predict minor variations easily. - Trusting complexity rules instead of length. That
P@ssw0rd1!from earlier sails through most legacy policies and still falls fast in practice. - Storing passwords insecurely. Plain-text notes, spreadsheets, and emailed password lists defeat the purpose. Use the password manager you already chose.
- Rotating on a schedule. Forced quarterly changes push people toward predictable increments of the same base password — the exact behavior NIST’s guidance exists to prevent. Change passwords when there’s evidence of compromise, not when the calendar says so.
- Skipping MFA because the password is strong. A strong password defends against guessing; MFA defends against the password being stolen. They cover different failure modes, which is why guidance treats them as a pair.
When Strong Passwords Aren’t Enough: MFA and Passkeys
Strong passwords are one layer, not a complete defense. Two developments matter for anyone deciding how far to go.
Multi-factor authentication closes the stolen-password gap. If a phisher captures your password or a breach leaks it, a second factor — an app code, a security key, or a biometric — still blocks the login. NIST builds this into its assurance levels: authentication at its AAL2 level requires two distinct factors, and the guidelines push verifiers to offer phishing-resistant options. CISA and the FTC both frame MFA as the companion step to strong passwords rather than an optional extra.
Passkeys are edging out passwords where they’re supported. A passkey is a cryptographic credential stored on your device and unlocked with your fingerprint, face, or device PIN. Because the passkey never leaves your device and is bound to the specific website, it can’t be phished the way a typed password can, and there’s nothing to reuse or leak in a breach.
Major platforms and browsers now support them, and adoption is growing on consumer services. The practical stance for 2026: use passkeys where a service offers them and you’re comfortable, and keep a strong, unique password plus MFA everywhere else. NIST’s guidance already accommodates these authenticator types at its higher assurance levels, and CISA’s MFA recommendations point in the same direction.
FAQ
How long should a password be in 2026?
At least 16 characters for accounts that matter most, following CISA’s consumer guidance. NIST requires a minimum of 15 characters for passwords used as the single authentication factor and permits at least 8 characters when a password is paired with MFA; it also wants systems to accept passwords of at least 64 characters so long passphrases work. Where a site caps you lower than that, use the longest random string it allows plus MFA.
Are password managers safe to use?
Yes, for most people they’re a net safety gain, and both CISA and the FTC recommend them. A reputable password manager encrypts your vault locally, and using one makes long, random, unique passwords practical across every account — something memory alone can’t do. The trade-offs are real but manageable: you must protect the master password, and the manager’s vendor is a target, which is a reason to choose a well-reviewed product and keep its software updated rather than a reason to keep passwords in a spreadsheet.
Do I really need to change my password every 90 days?
No. Current NIST guidance explicitly prohibits requiring periodic password changes and says to force a change only when there’s evidence of compromise. Scheduled rotation tends to produce predictable variations of the same password, which attackers anticipate. The exceptions that do demand an immediate change: a service notifies you of a breach involving your account, a breached-password check flags your password, or you have any reason to believe someone else knows it.
Are passphrases better than passwords?
A passphrase is just a password made of words, so the question is really about construction. A passphrase of 5–7 truly unrelated words meets CISA’s definition of strong and is much easier to memorize — ideal for your password manager’s master password and any other password you must type from memory. A passphrase built from a quote, lyric, or predictable word sequence is weak no matter how long it is. For accounts you never type manually, a fully random generated string is at least as good.
Does a strong password protect against phishing?
No. Phishing doesn’t attack the password; it collects it — you type your real credentials into a fake login page, and the attacker uses them immediately. That’s why strong-password guidance from NIST, CISA, and the FTC consistently arrives paired with MFA, and why phishing-resistant methods such as passkeys and hardware security keys are the stronger upgrade when a service supports them.
How can I check whether my password has been breached?
Use the Pwned Passwords service at Have I Been Pwned, which lets you search a corpus of passwords that have appeared in data breaches. It’s the same privacy model described earlier: only the first five characters of a locally computed hash leave your browser, and the full comparison happens on your side. Most major password managers integrate the same dataset and will flag saved passwords for you automatically. If a password you use anywhere shows up as breached, change it on every account where it appears — starting with your email.
Are passkeys going to replace passwords?
Partially, and gradually. Passkeys are phishing-resistant, unique by construction, and increasingly supported across major platforms and consumer services, so they will keep displacing passwords where they’re offered. But passwords remain the near-universal fallback — nearly every service still accepts one, and not every device or situation fits passkey workflows yet. The practical approach is to adopt passkeys where available and keep strong, unique passwords with MFA everywhere else.
Conclusion
Strong passwords are important because passwords are still the front door to nearly every account, and weak or reused ones hand attackers that door on a plate — even though, as the 2026 Verizon DBIR shows, unpatched software flaws have now joined stolen credentials at the top of the breach-entry-point list. The definition of strong is longer and simpler than the old complexity rules suggested: at least 16 characters, generated randomly, and used on exactly one account, backed by MFA and a breached-password check.
The practical next step fits into a single sitting: install a password manager, replace the passwords on your email, financial, and other critical accounts with generated 16-character random ones, turn on MFA — or a passkey where it’s offered — and stop rotating anything unless there’s evidence of compromise. A strong password still can’t stop phishing, so treat MFA as part of the password’s strength rather than an optional add-on. That combination — length, randomness, uniqueness, and a second factor — is about as solid a foundation as most people can build in an afternoon.
You May Also Like
 Data Security & Privacy
Tokenization vs Encryption: Key Differences and Best Practices
 Data Security & Privacy
How Encryption Works: A Practical Guide to Data Encryption Best Practices
 Data Security & Privacy
Endpoint Security vs Antivirus: Key Differences for Better Protection
 Network Security
What is Penetration Testing and Why Is It Crucial for Your Cybersecurity Strategy?
 Network Security
11 Best Free Penetration Testing Tools: Your Complete Guide for 2027
 Cybersecurity
What Is Endpoint Management? A Practical Guide for Modern Teams
 Data Security & Privacy
The Importance of Vulnerability Management and Attack Surface Management
 Cybersecurity
Effective Strategies for Prioritizing Cybersecurity Vulnerability Remediation
 Web Development
